FussMobile Kapitan™
 KAPITAN FussMobile
Managed Kubernetes for environments
where failure is not an option.
Purpose-built for disconnected, airgapped edge environments. Proven at scale across the world's leading cruise lines.
The platform
One platform. Three managed services.
Kapitan delivers complete managed edge infrastructure — from cluster operations to object storage to application hosting. Your team focuses on outcomes. Kapitan manages the platform.
Kapitan Platform
Fully managed Kubernetes clusters at the edge — provisioned, operated, and maintained end-to-end by FussMobile. Designed for multi-tenant, multi-brand environments with automated delivery, continuous self-healing, and 24/7 incident ownership.
- Automated cluster provisioning and lifecycle management
- GitOps-driven workload delivery across the entire fleet
- Multi-tenant namespace isolation per brand and environment
- Automated certificate management and secret rotation
- Continuous backup — control plane, persistent volumes, cluster state
- Full observability stack: metrics, logs, alerting, uptime monitoring
- OIDC-based access control with role-based namespace scoping
- On-call incident response and post-incident review
Kapitan S3
Managed S3-compatible object storage deployed directly within each edge cluster — on dedicated, isolated infrastructure. Drop-in API compatibility means applications connect without modification. FussMobile manages capacity, replication, and availability.
- Dedicated storage infrastructure per cluster — isolated by design
- S3-compatible API — no application changes required
- Active-active replication for availability
- Dual access planes: application traffic and operational management
- Capacity management and storage lifecycle handled by FussMobile
- Airgap-native delivery — no internet dependency at runtime
Kapitan Messaging
Managed cluster infrastructure for enterprise secure messaging in maritime environments. FussMobile provides the platform — your messaging vendor deploys their application on top. A clear operational boundary: we own the infrastructure, they own the application.
- Managed Kubernetes cluster purpose-built for messaging workloads
- Persistent storage, networking, and TLS managed by FussMobile
- Supports relational database, cache, and MQTT messaging protocols
- Crew and guest WiFi traffic routing handled at the platform layer
- ISV application layer remains fully under vendor control
- Validated reference architecture for maritime enterprise messaging
Why Kapitan
Built for environments that don't forgive mistakes.
Maritime edge is not a cloud environment with a few quirks. It is a fundamentally different operational reality — and Kapitan is the only managed Kubernetes platform designed for it.
Airgap-native from the ground up
Kapitan is designed to operate without reliable internet connectivity. Workload delivery, certificate renewal, storage operations, and cluster self-healing all function in fully disconnected environments. Connectivity is treated as a variable, not a dependency.
Multi-tenant, multi-brand by design
A single Kapitan deployment supports multiple independent business units simultaneously — with complete isolation between tenants, separate operational visibility per brand, and a unified management plane for the operator. One platform, many brands, no compromise.
Production-proven at fleet scale
Kapitan is not a reference architecture or a pilot deployment. It is the active managed platform for one of the world's largest cruise fleets — 66 ships, three brands, four years of continuous operation, and a zero-incident track record. That history is the product.
Complete operational ownership
FussMobile holds incident ownership across the entire estate — not advisory, not escalation support, but full managed operations. Cluster provisioning, upgrade cadence, backup verification, on-call response, and post-incident review are all included. Your team is never on the hook for platform failures.
AI-native operations
When something breaks, Kapitan already knows why.
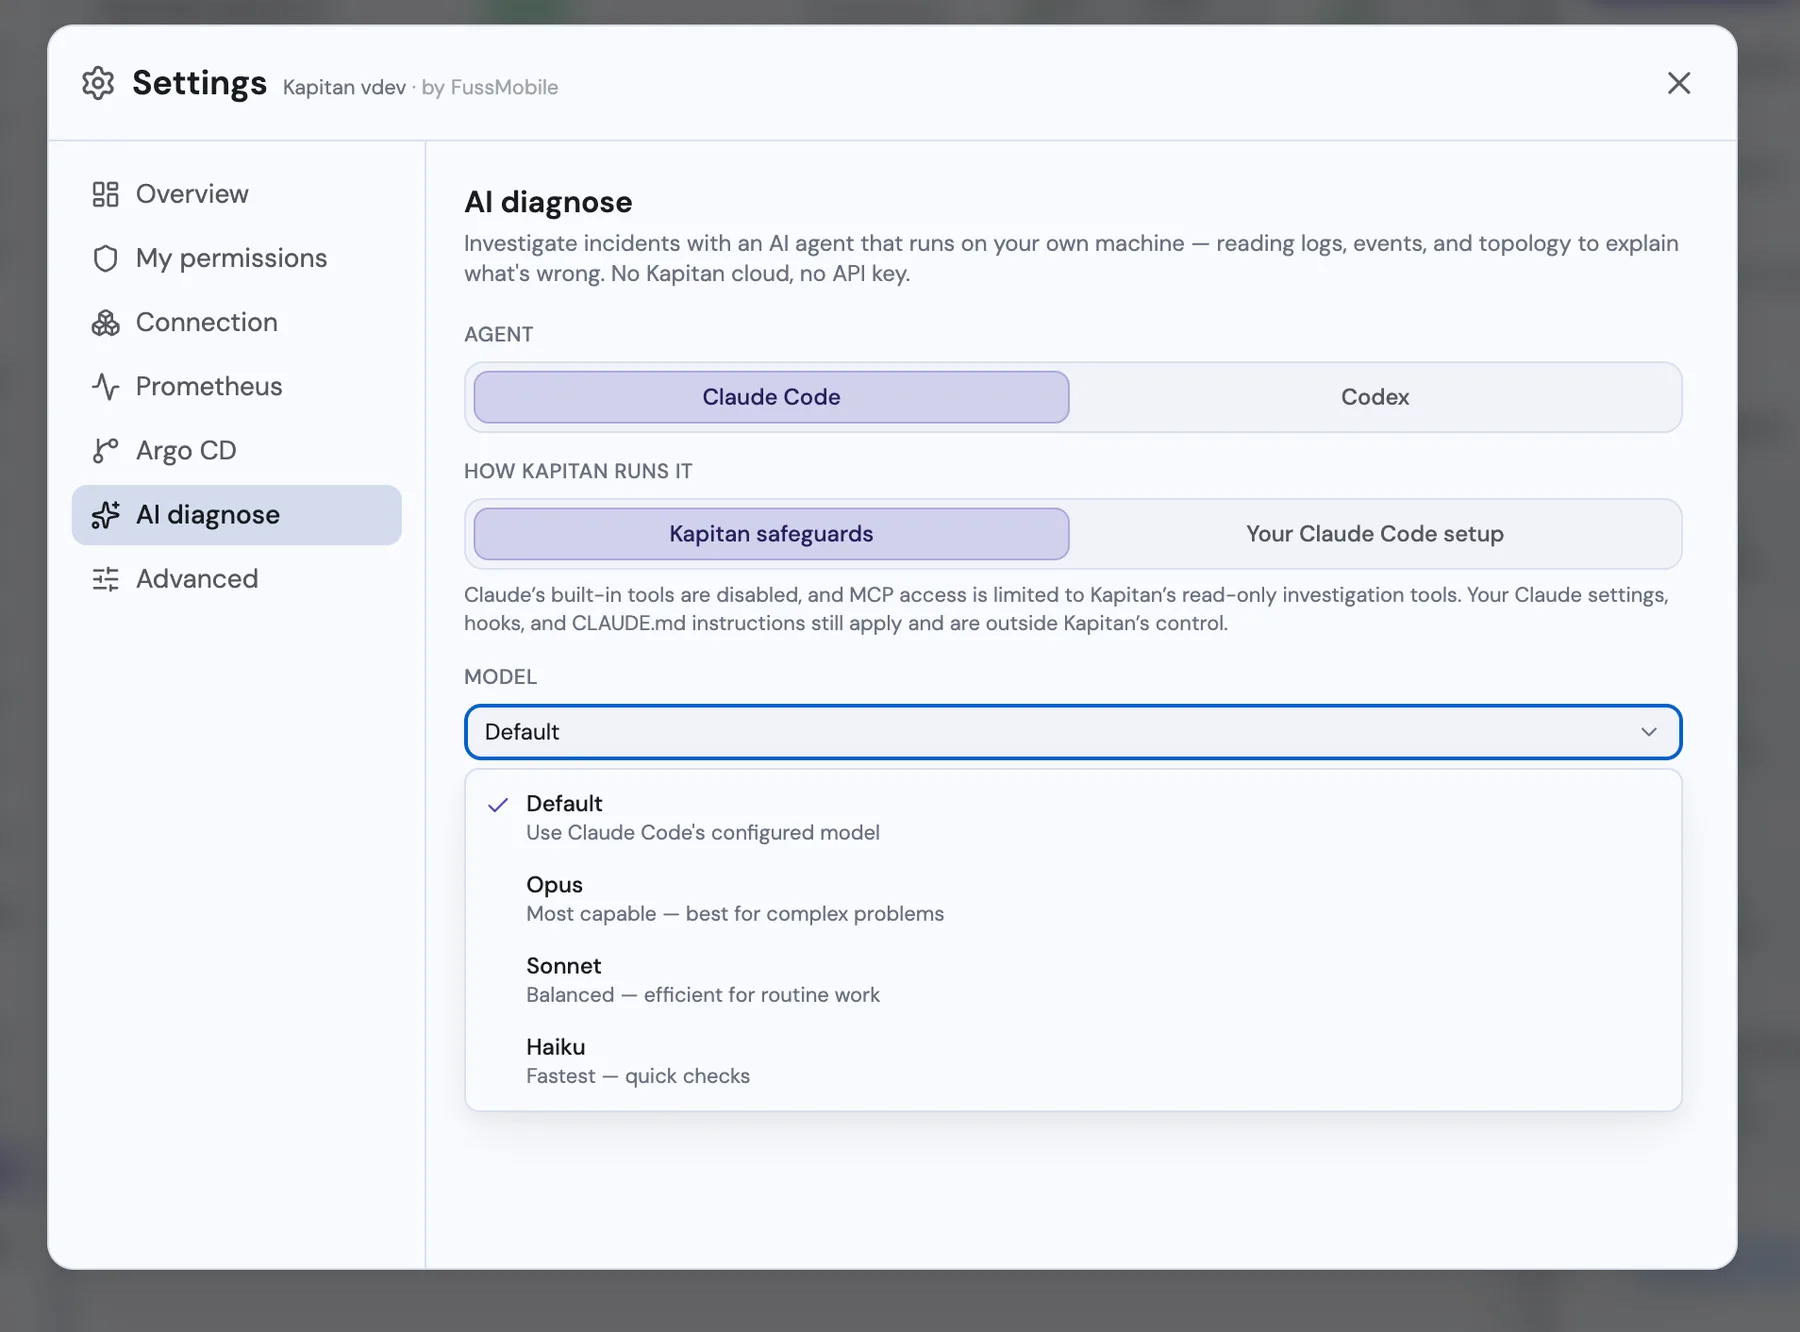
Every cluster Kapitan operates ships with an AI investigation agent built in — one that reads logs, events, and topology to explain what's wrong and how to fix it, in seconds, not an on-call escalation.
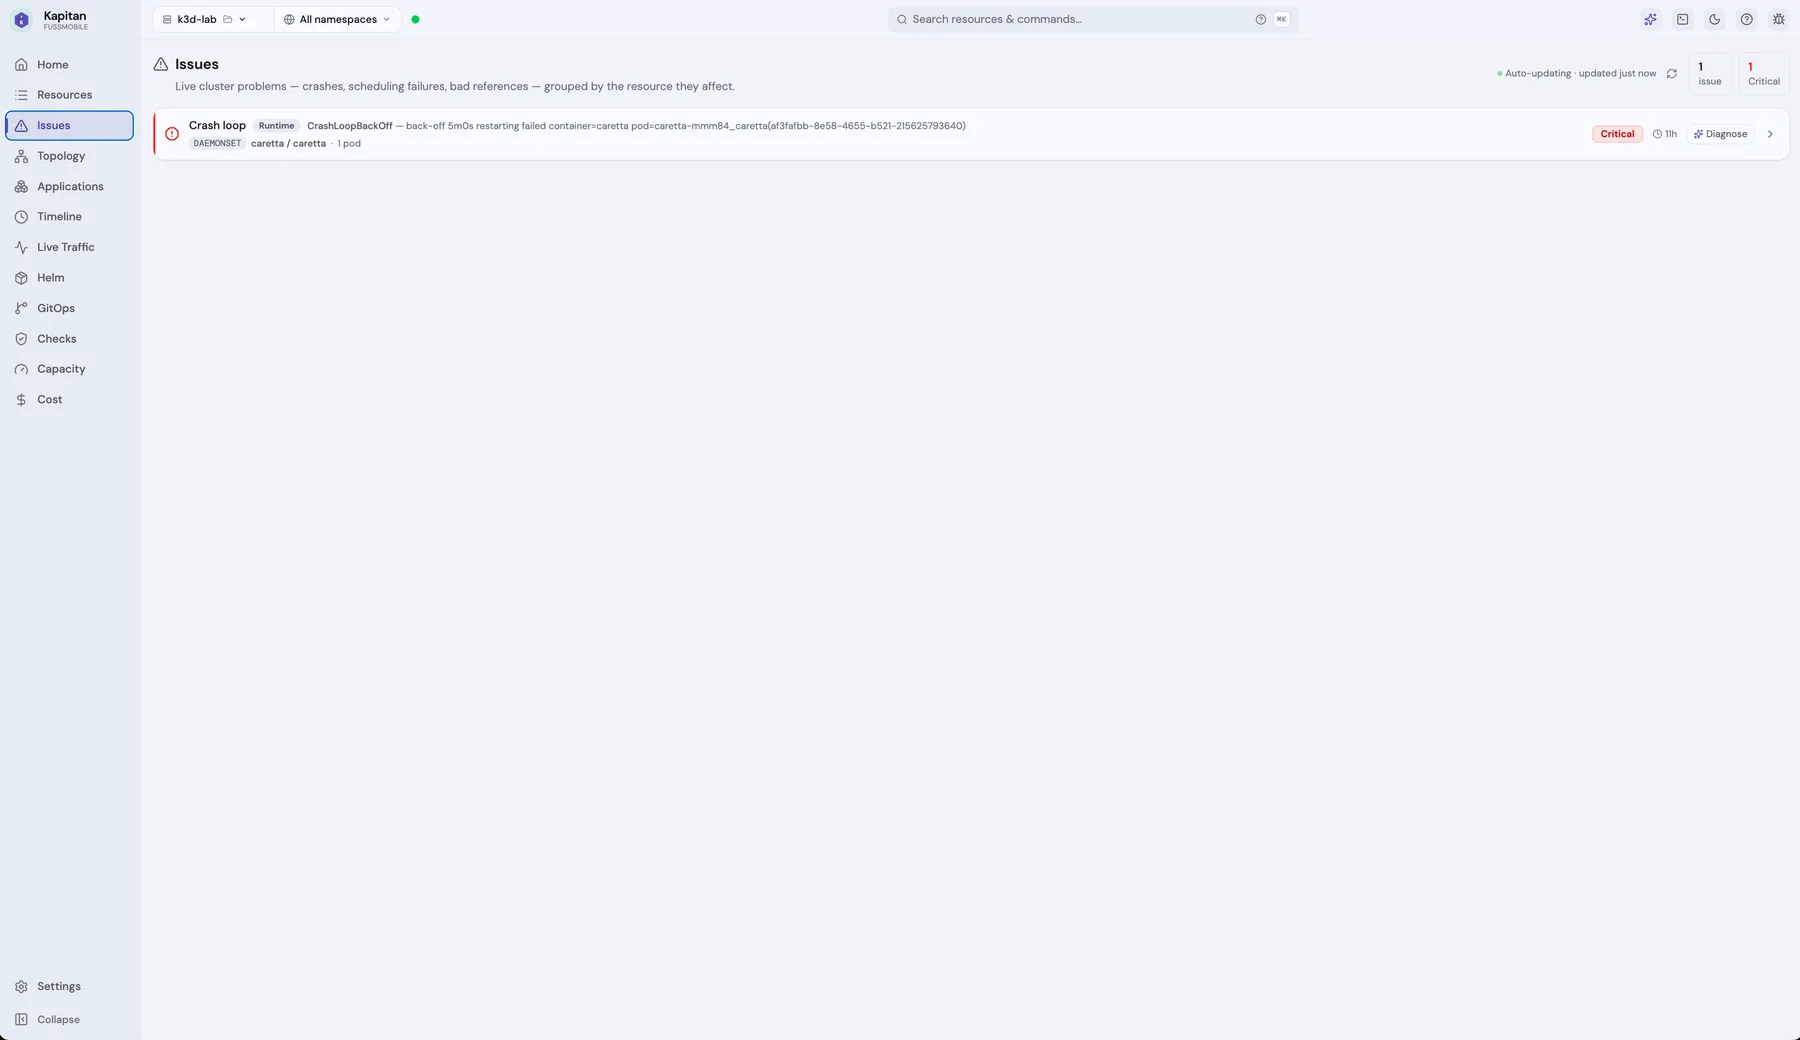
Detected
Kapitan surfaces the problem the moment it happens — grouped by the resource it affects, with what's wrong already summarized, not buried in a raw event stream.
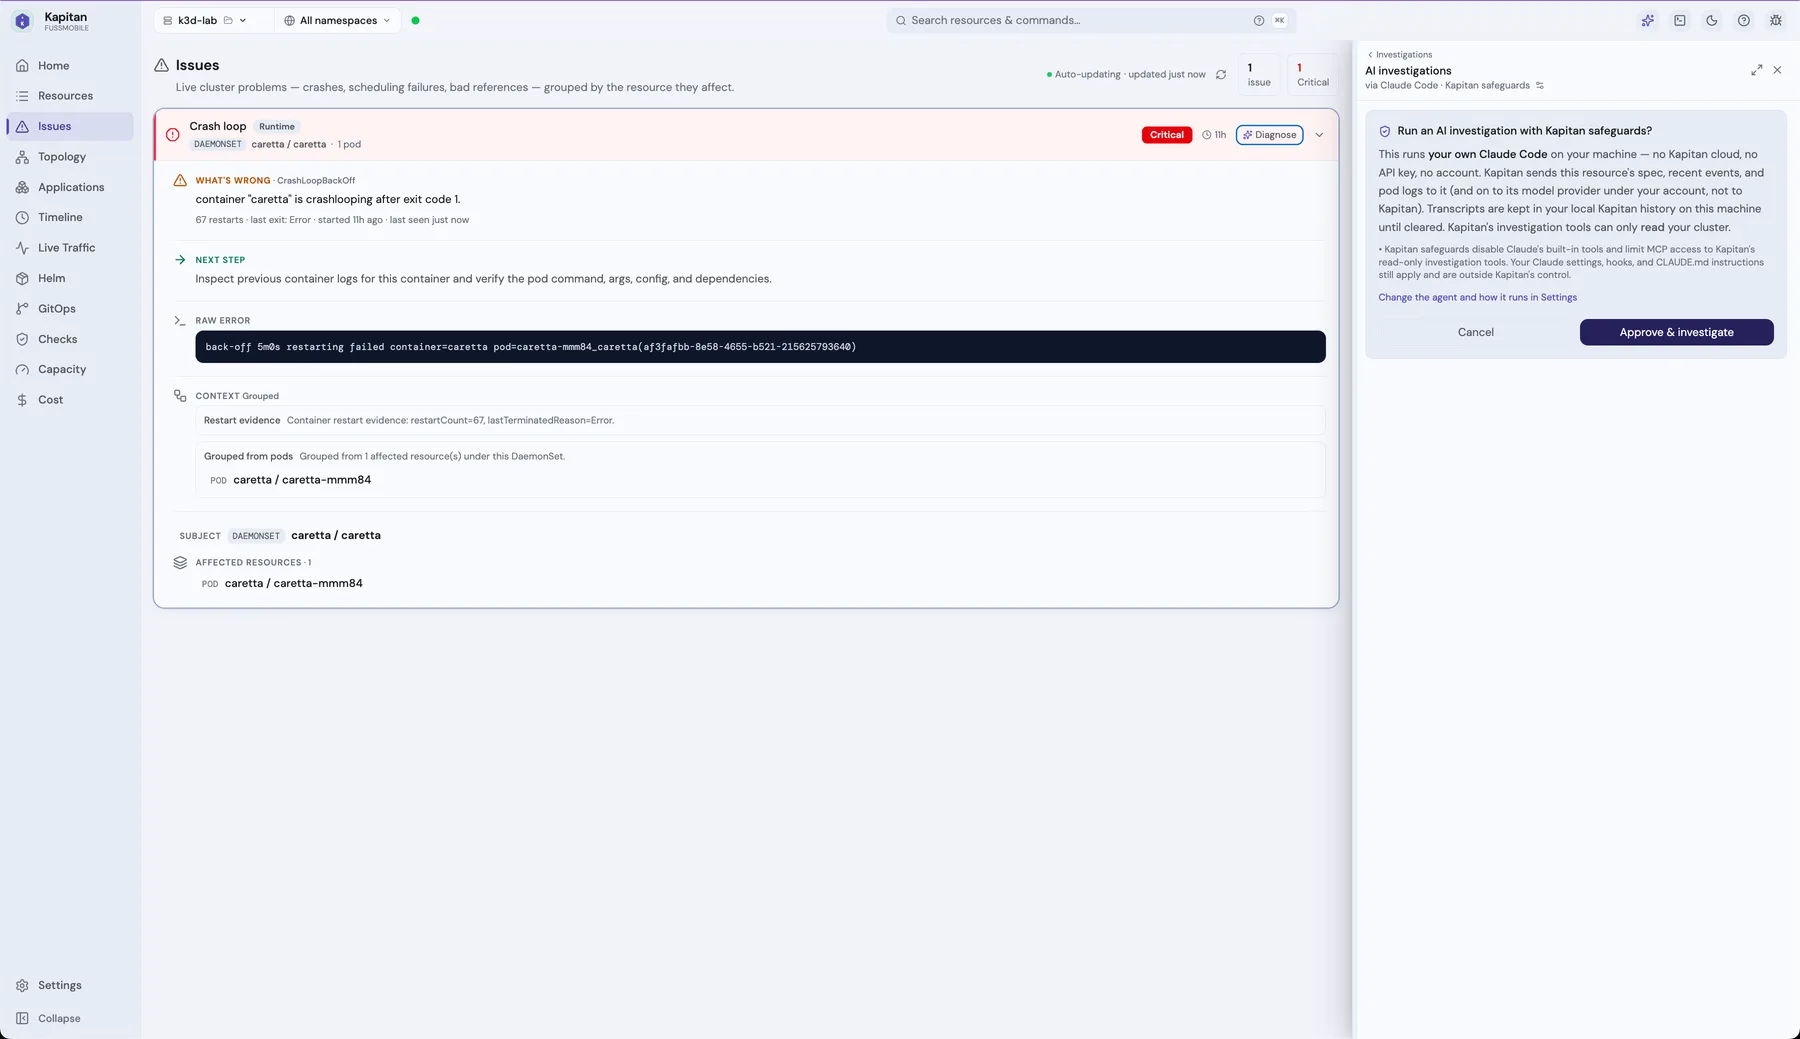
You approve
Nothing runs without explicit approval. The agent runs on your own machine, under your own account — never Kapitan’s cloud.
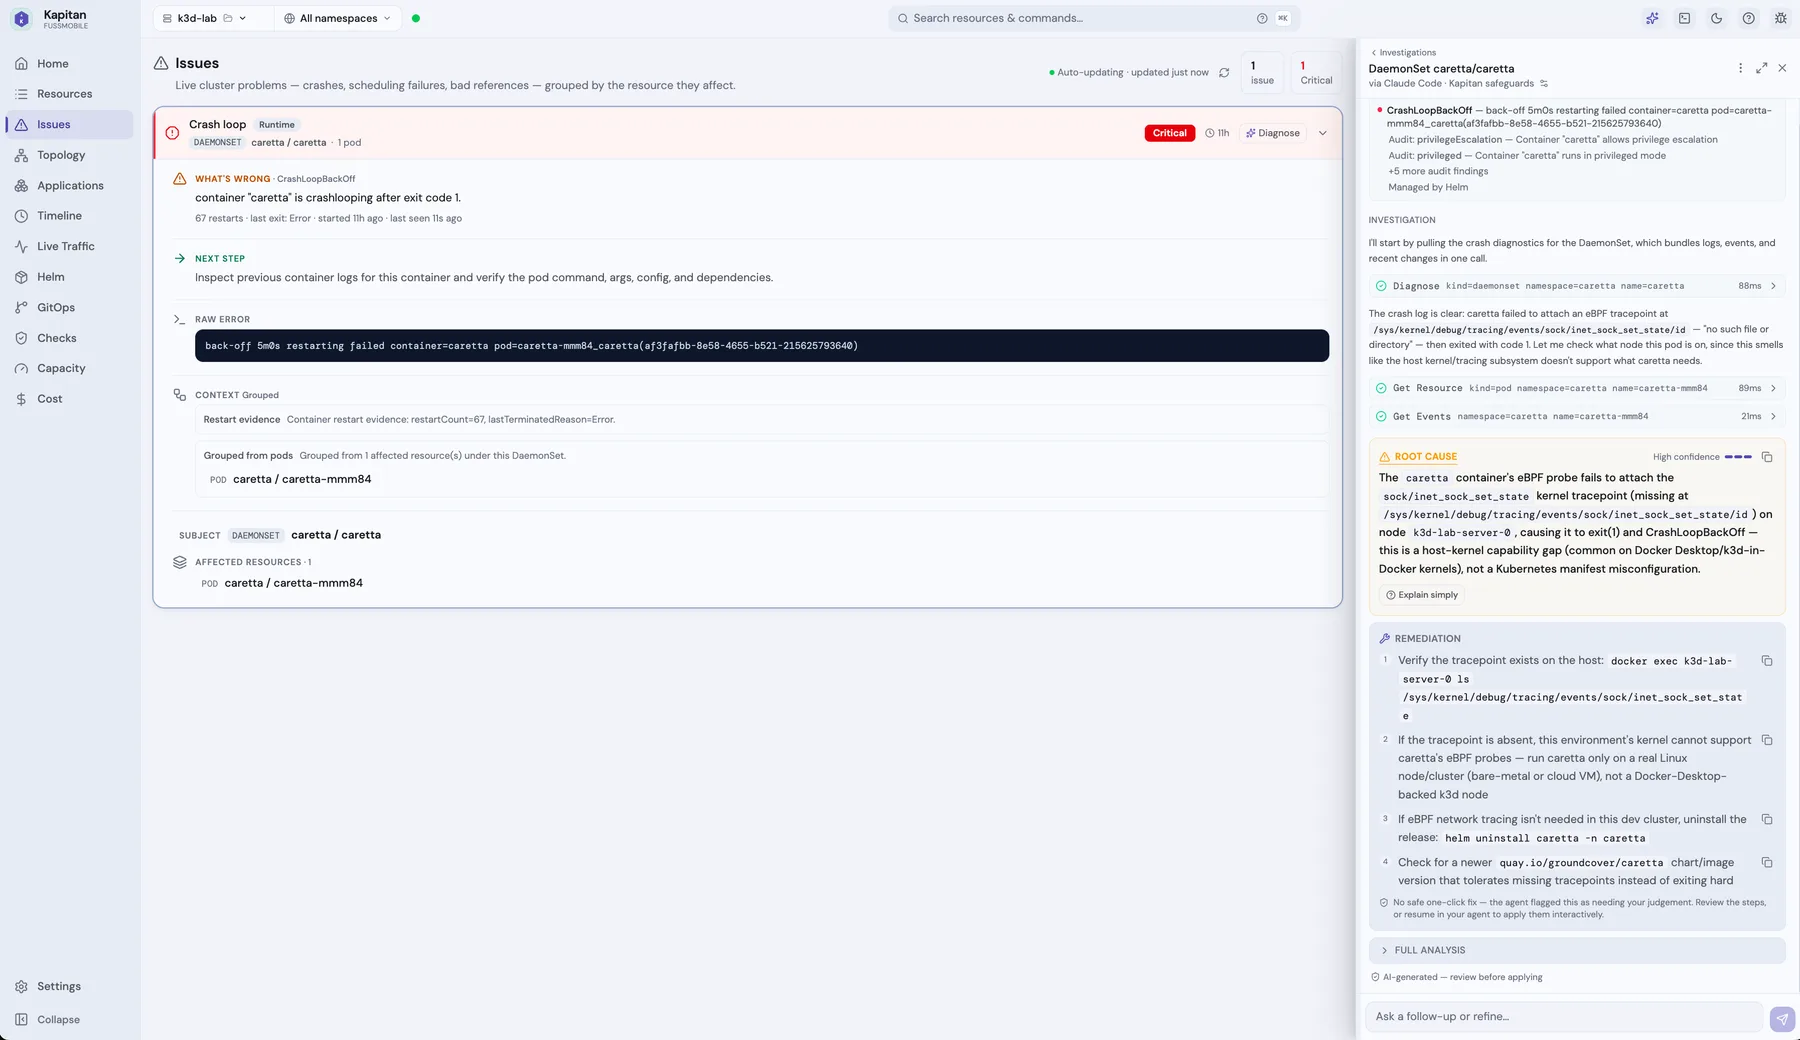
Root cause, not a guess
A confidence-scored root cause plus ready-to-run remediation commands — not a canned suggestion, a real read of the cluster.
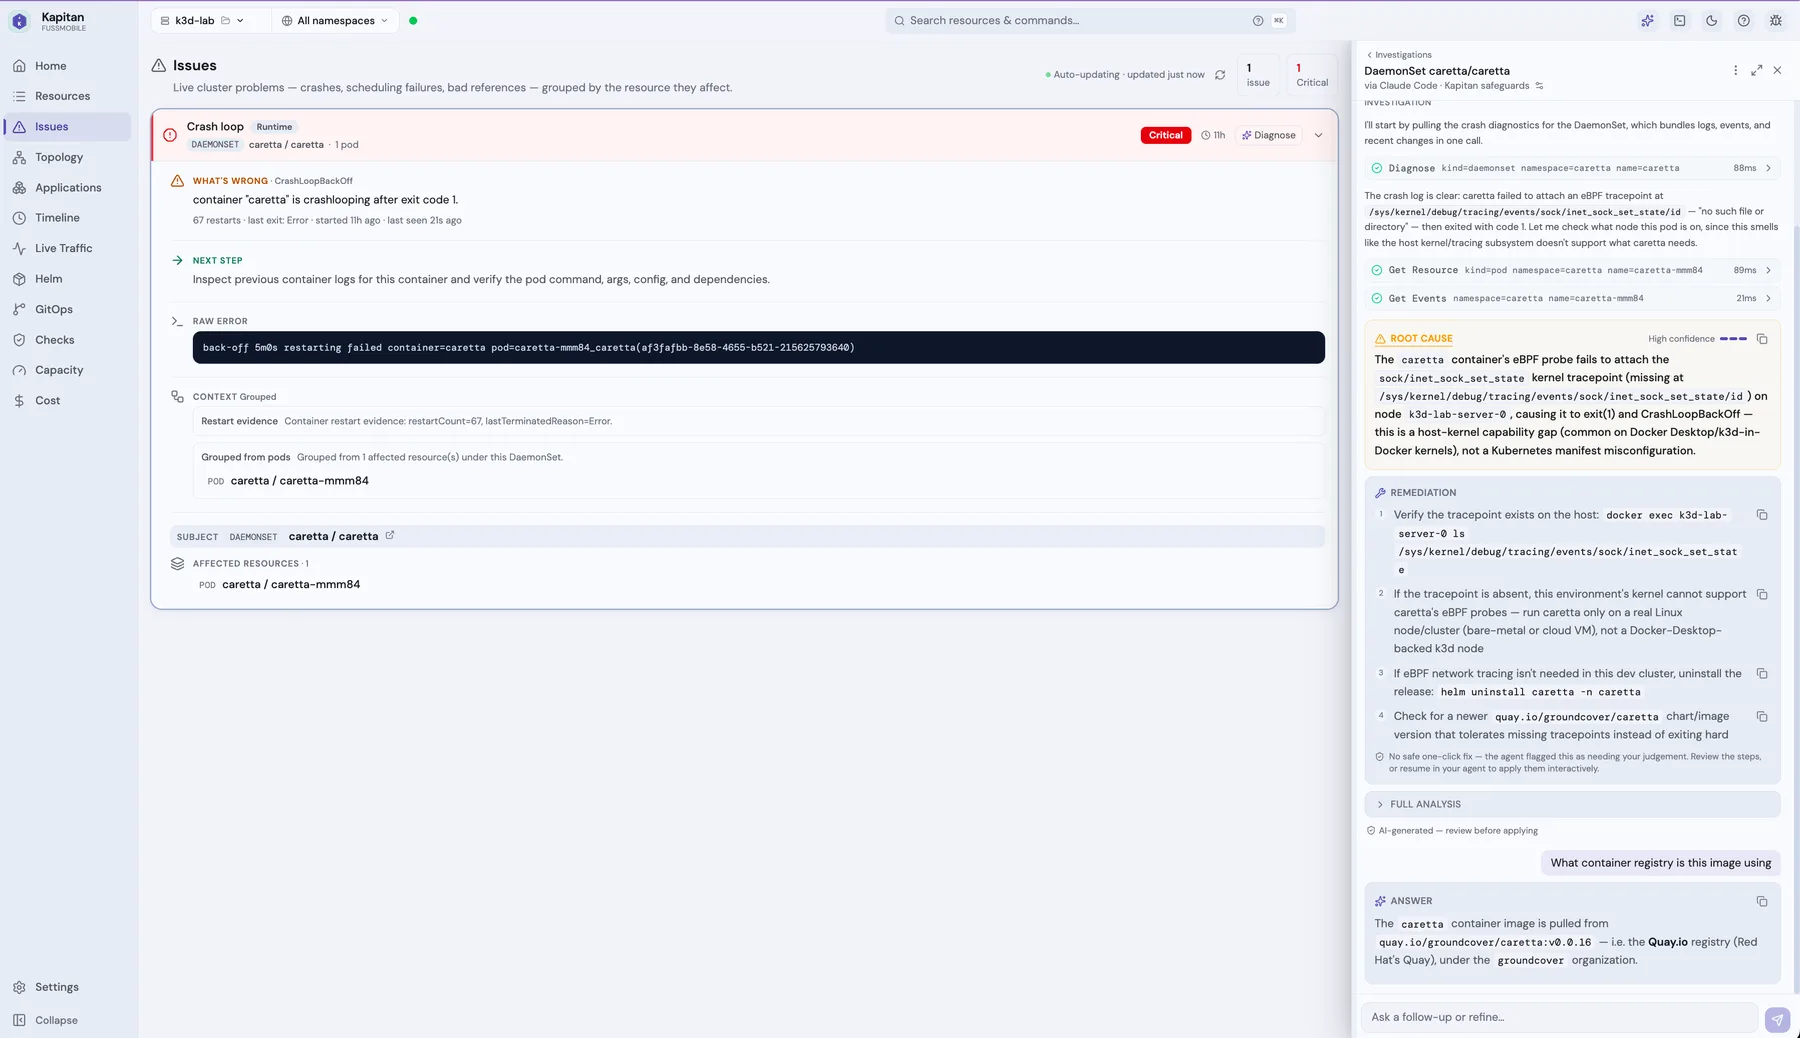
Keep asking
It’s a conversation. Ask a follow-up and it re-inspects the cluster to answer, in the same thread as the original investigation.
Built-in safeguards
Your data never leaves your control.
- Runs on your own machine, under your own agent account — no Kapitan cloud, no API key handed to Kapitan
- The agent's built-in tools are disabled; it can only read cluster state through Kapitan's own read-only investigation tools
- Every investigation is kept in your local history until you clear it — Kapitan doesn't retain a copy
- Choose your own agent and model tier — the fastest model for routine checks, the most capable for anything complex
Capabilities
Enterprise-grade operations.
Maritime-hardened delivery.
Every Kapitan capability is validated at scale across a live production fleet. What follows is what we operate — not what we plan to build.
Fleet-wide delivery
Workload and configuration changes propagate across the entire fleet automatically — with rollback capability and full audit trail.
Disconnected operation
Clusters operate independently when connectivity is unavailable. Reconnection triggers reconciliation without manual intervention.
Managed object storage
S3-compatible storage deployed within each cluster — capacity, replication, and access managed entirely by FussMobile.
Full-stack observability
Metrics, logs, alerting, and uptime monitoring across every cluster in the fleet — unified visibility for the operator, scoped views per brand.
Zero-touch certificate management
TLS certificates issued, rotated, and renewed automatically across all clusters and ingress endpoints. Expiry is never an operational event.
New environment onboarding
A proven, repeatable onboarding process brings new ships or edge sites onto the platform in days — not weeks. Three phases, fully documented, zero improvisation.
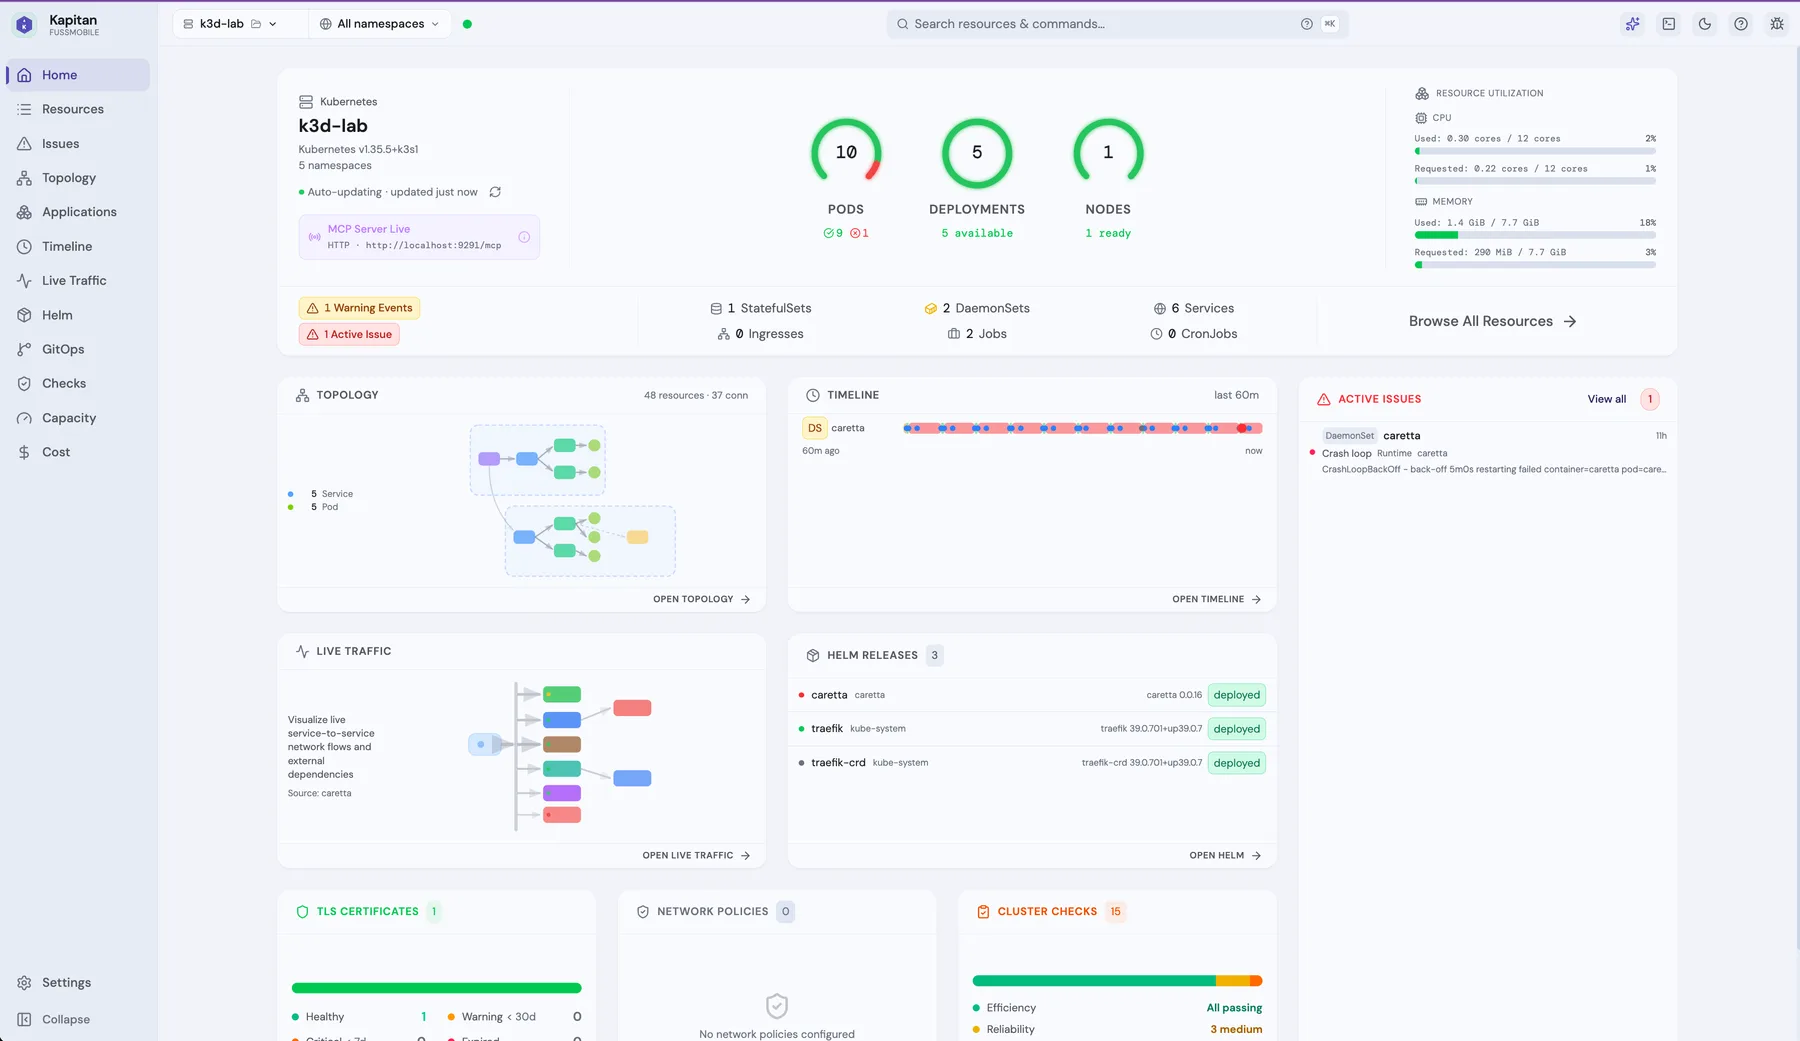
Inside the console
This is what your team actually looks at.
Screenshots from a live Kapitan test cluster — the same console your operators and ours share, not a mockup.
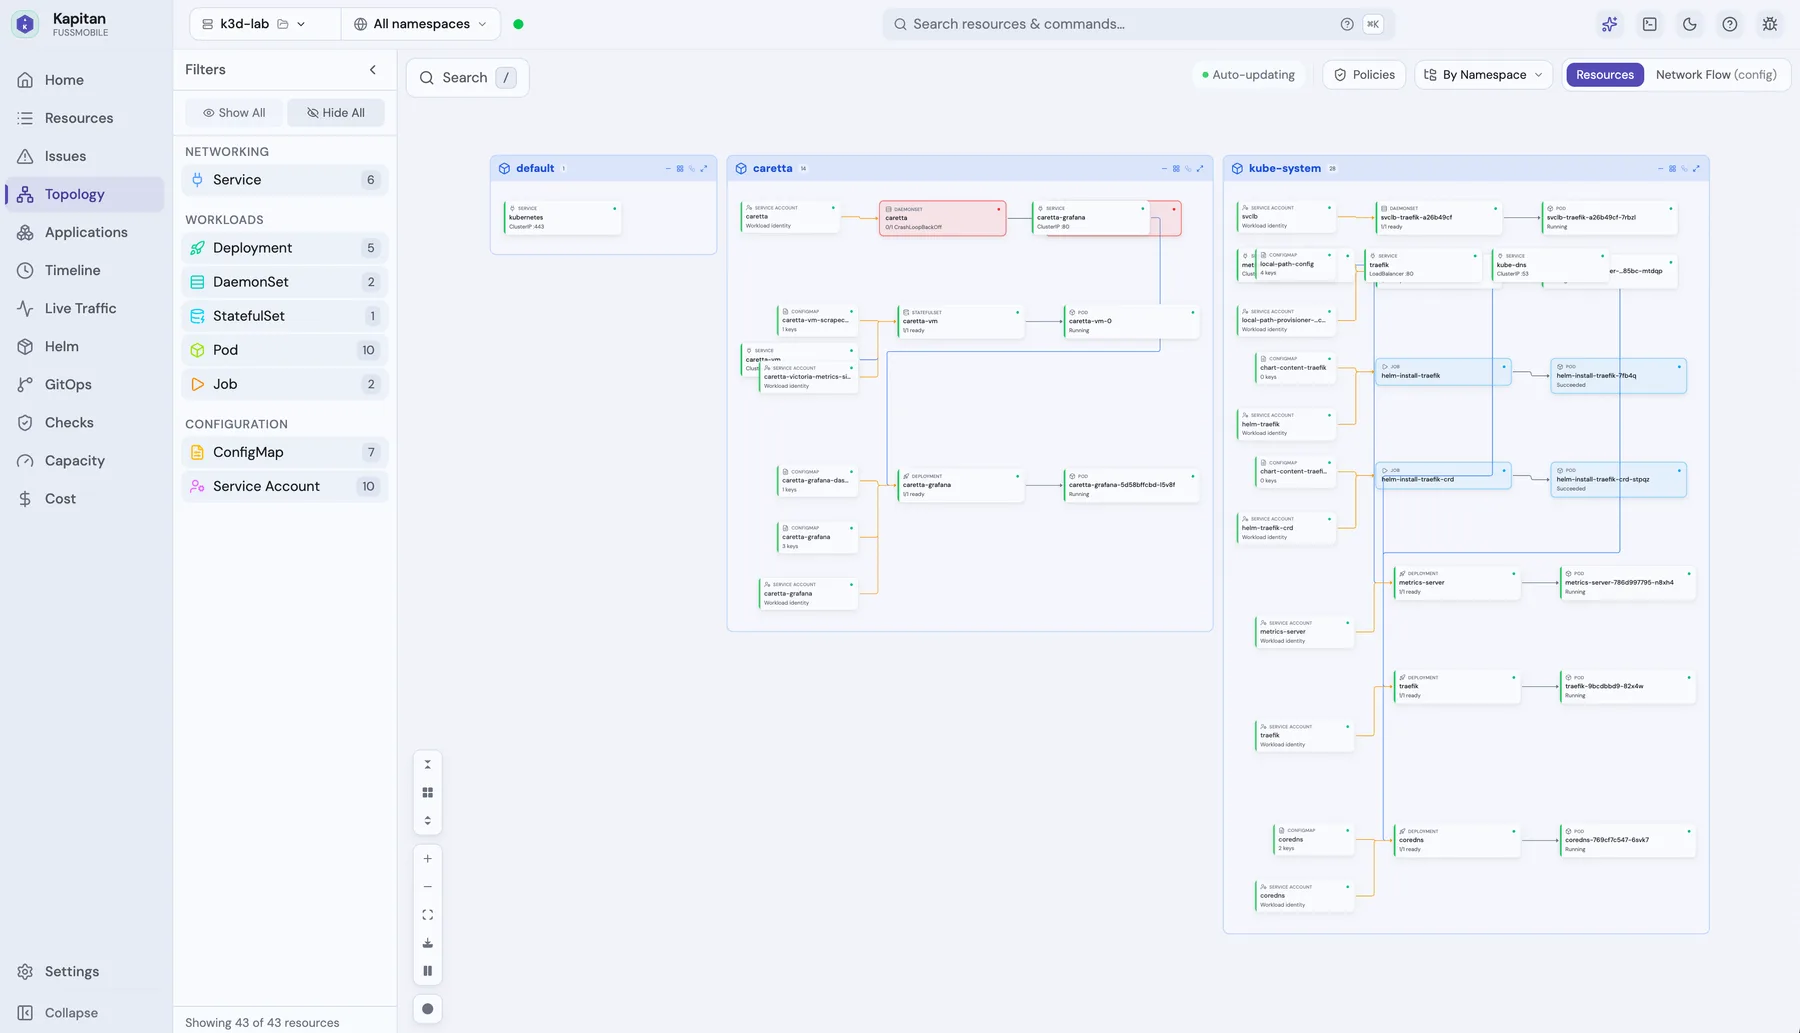
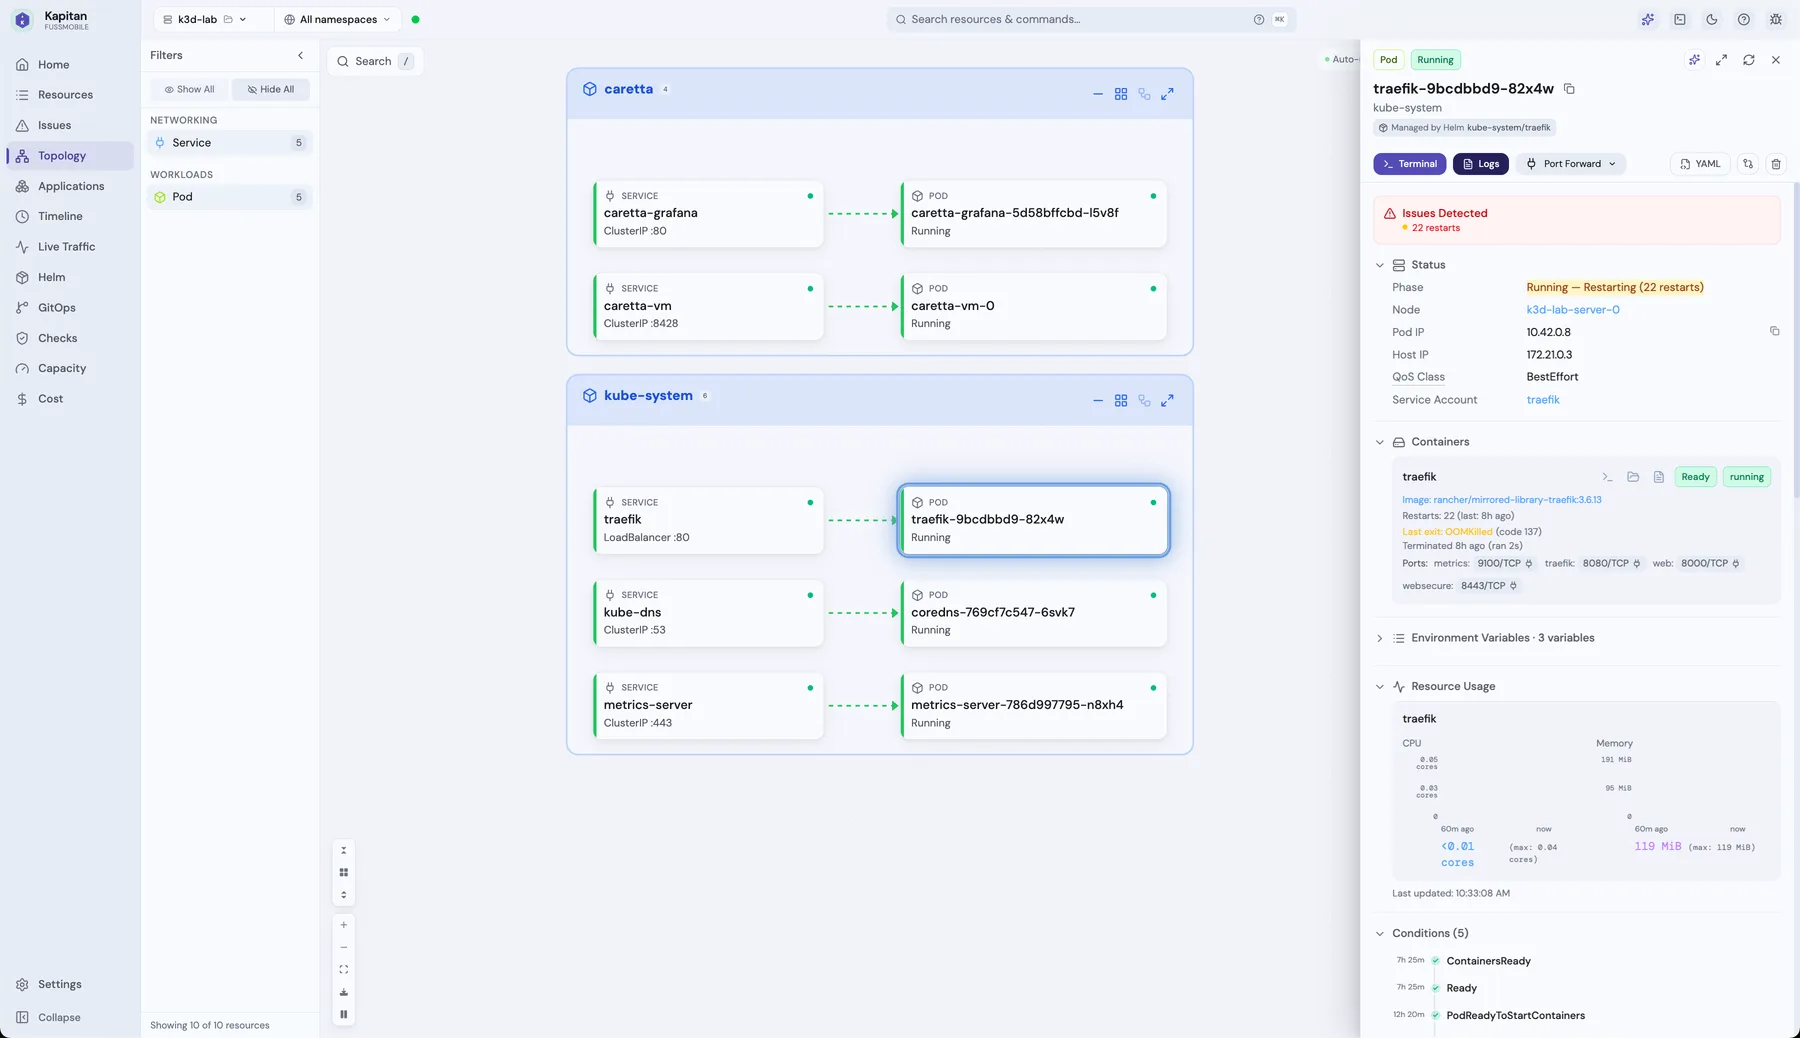
See the whole cluster, live
Every workload, service, and dependency mapped automatically. Drill into any node down to live logs and resource usage without leaving the graph.
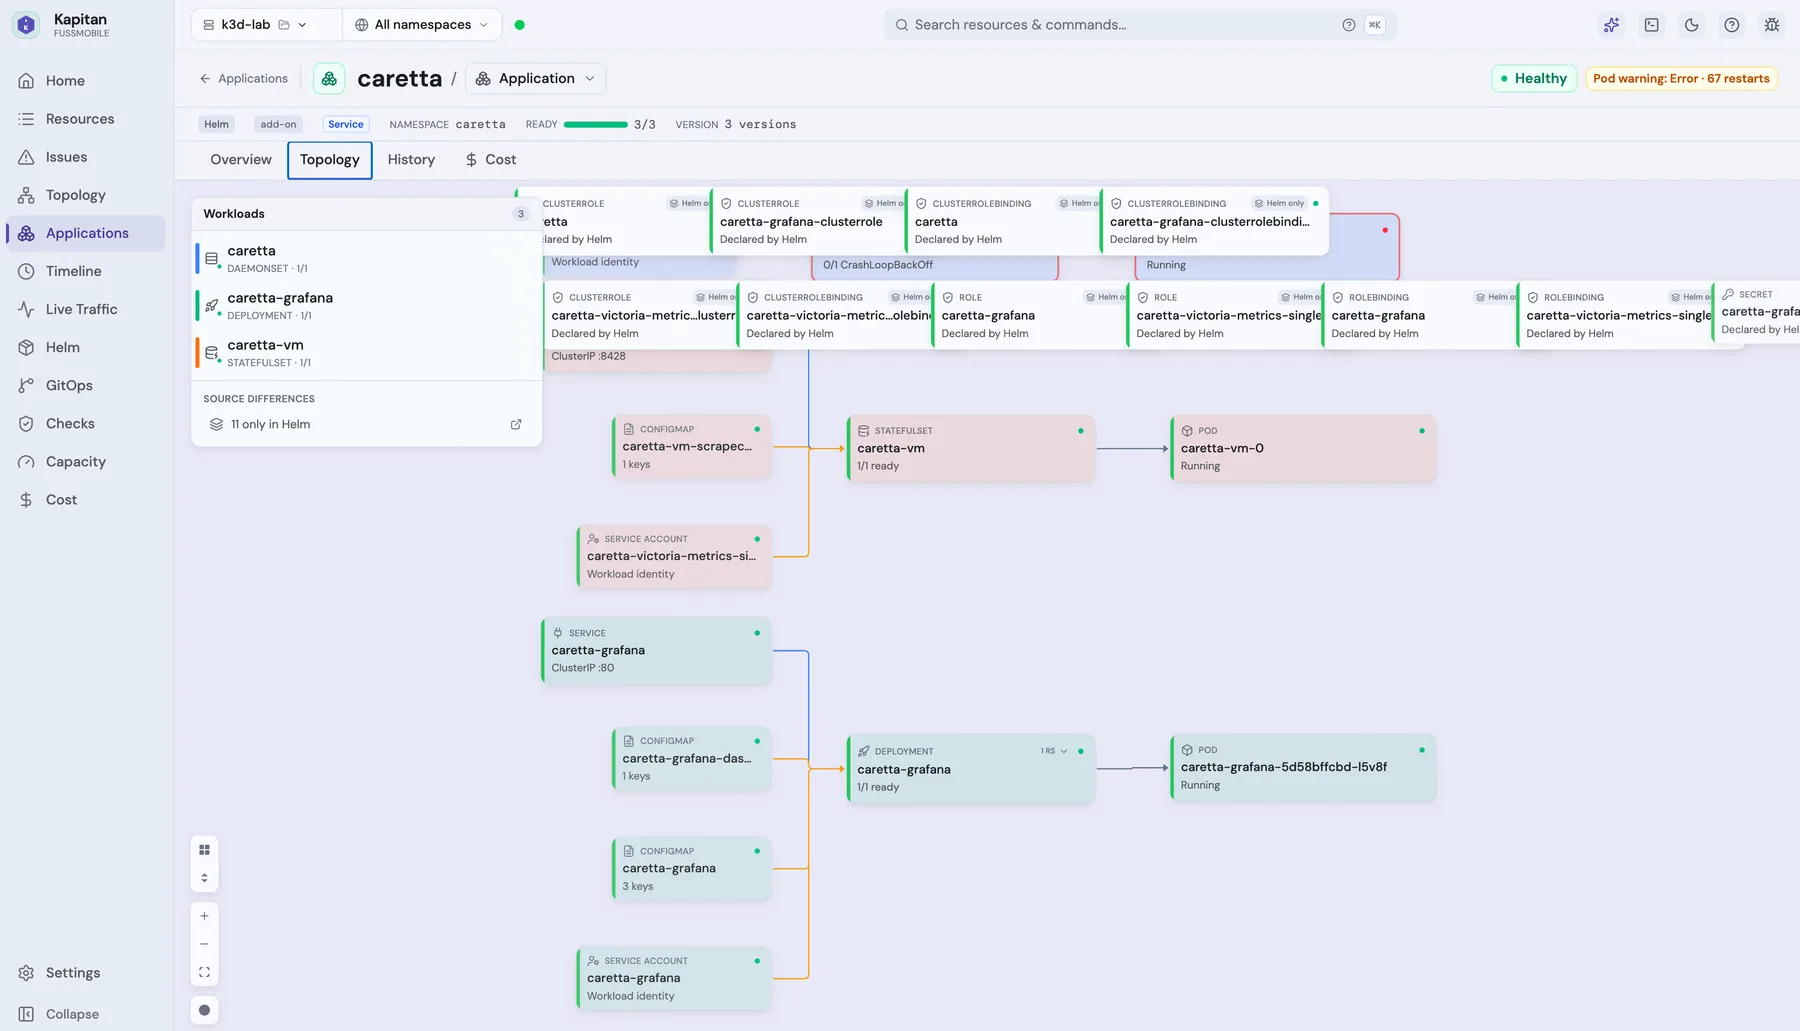
Health, per application
Every workload, config, and secret a release owns is grouped into one health view — so a crash reads as "this app has a problem," not a wall of unrelated resources.
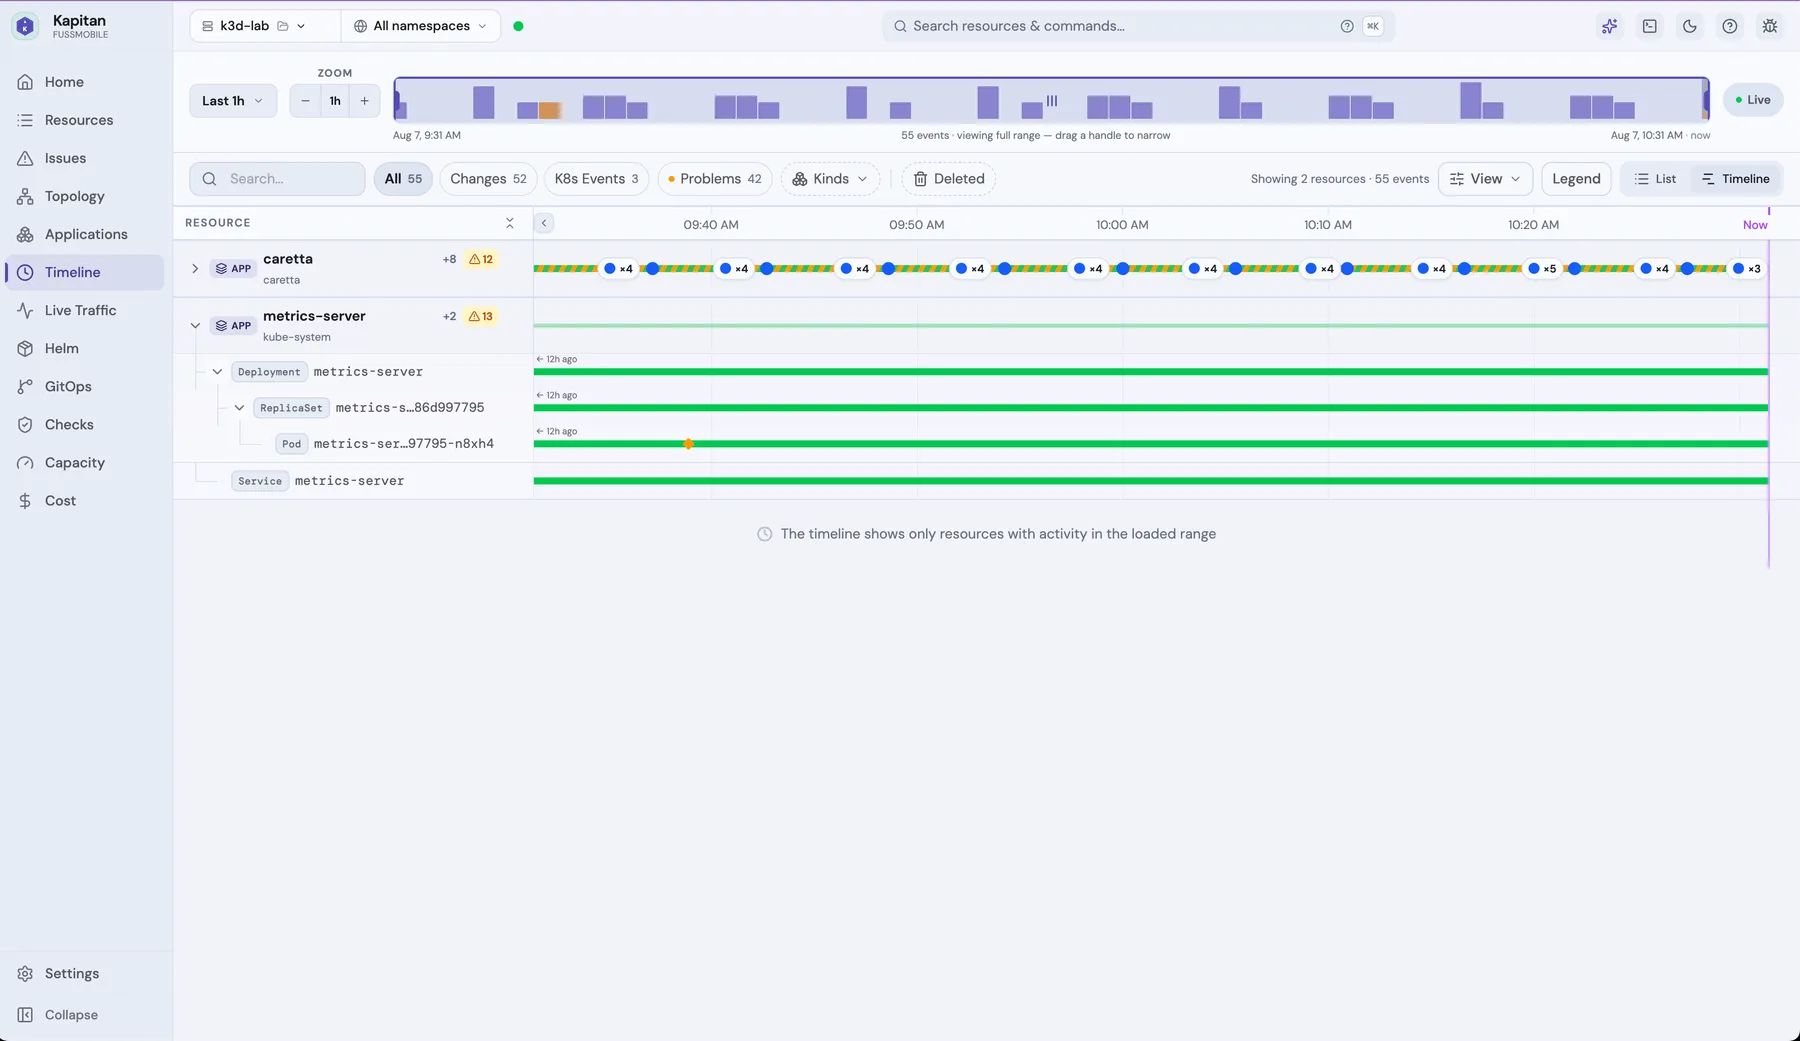
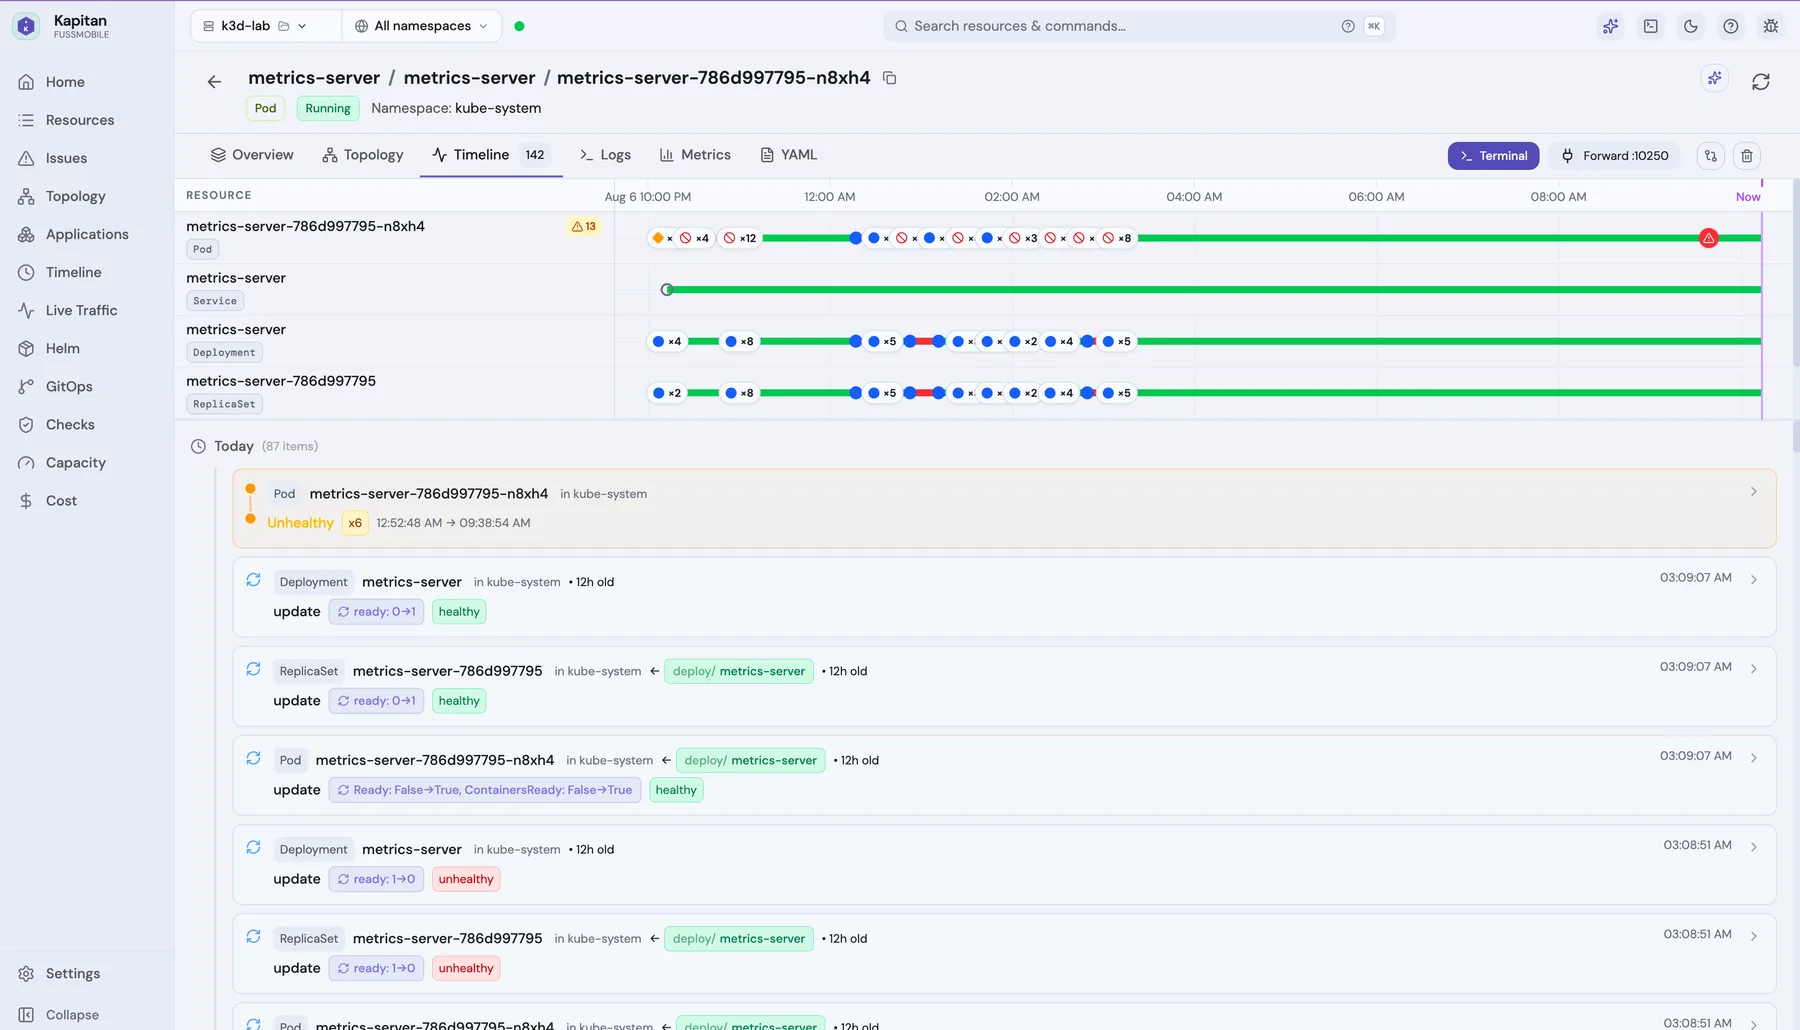
A timeline for every resource
Every change, restart, and event across the cluster — filterable by resource, namespace, or problem — so "what changed right before this broke" is a five-second lookup.
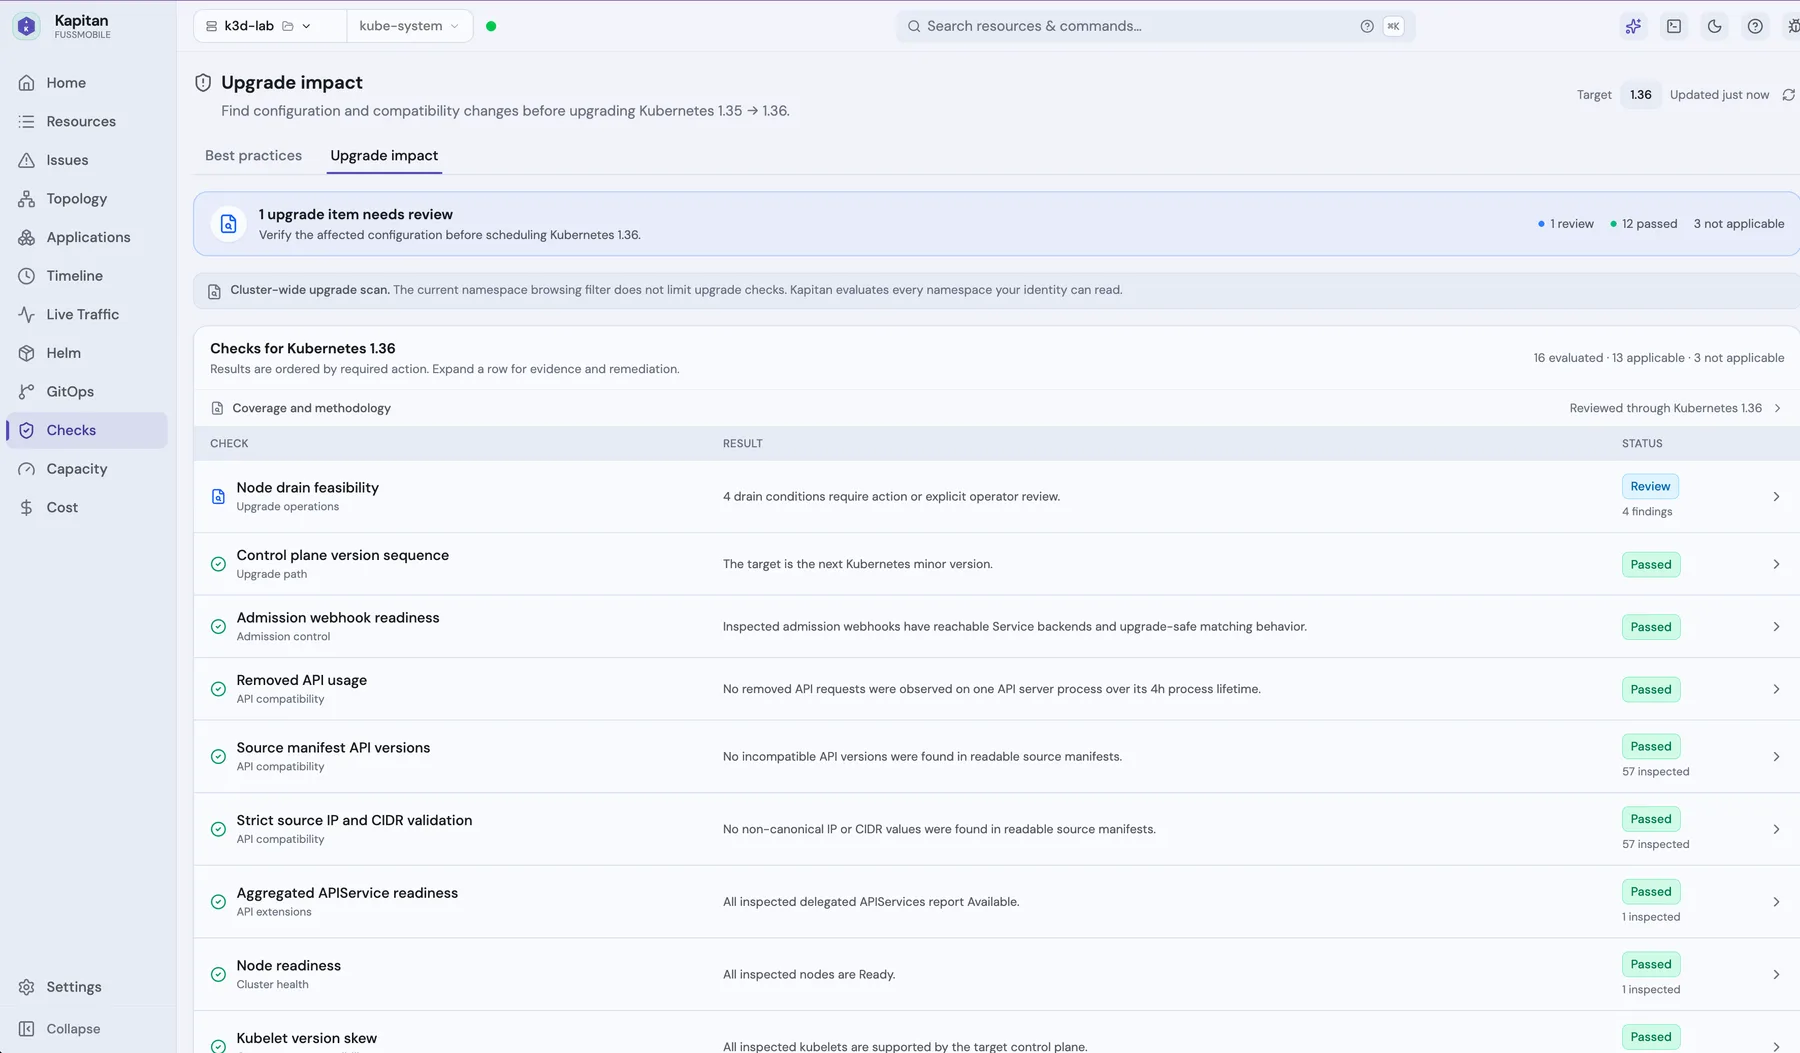
Upgrades that don't gamble with production
Before any control-plane upgrade, Kapitan scans for drain feasibility, deprecated API usage, and admission-webhook readiness — flagging exactly what needs review before you schedule the change.
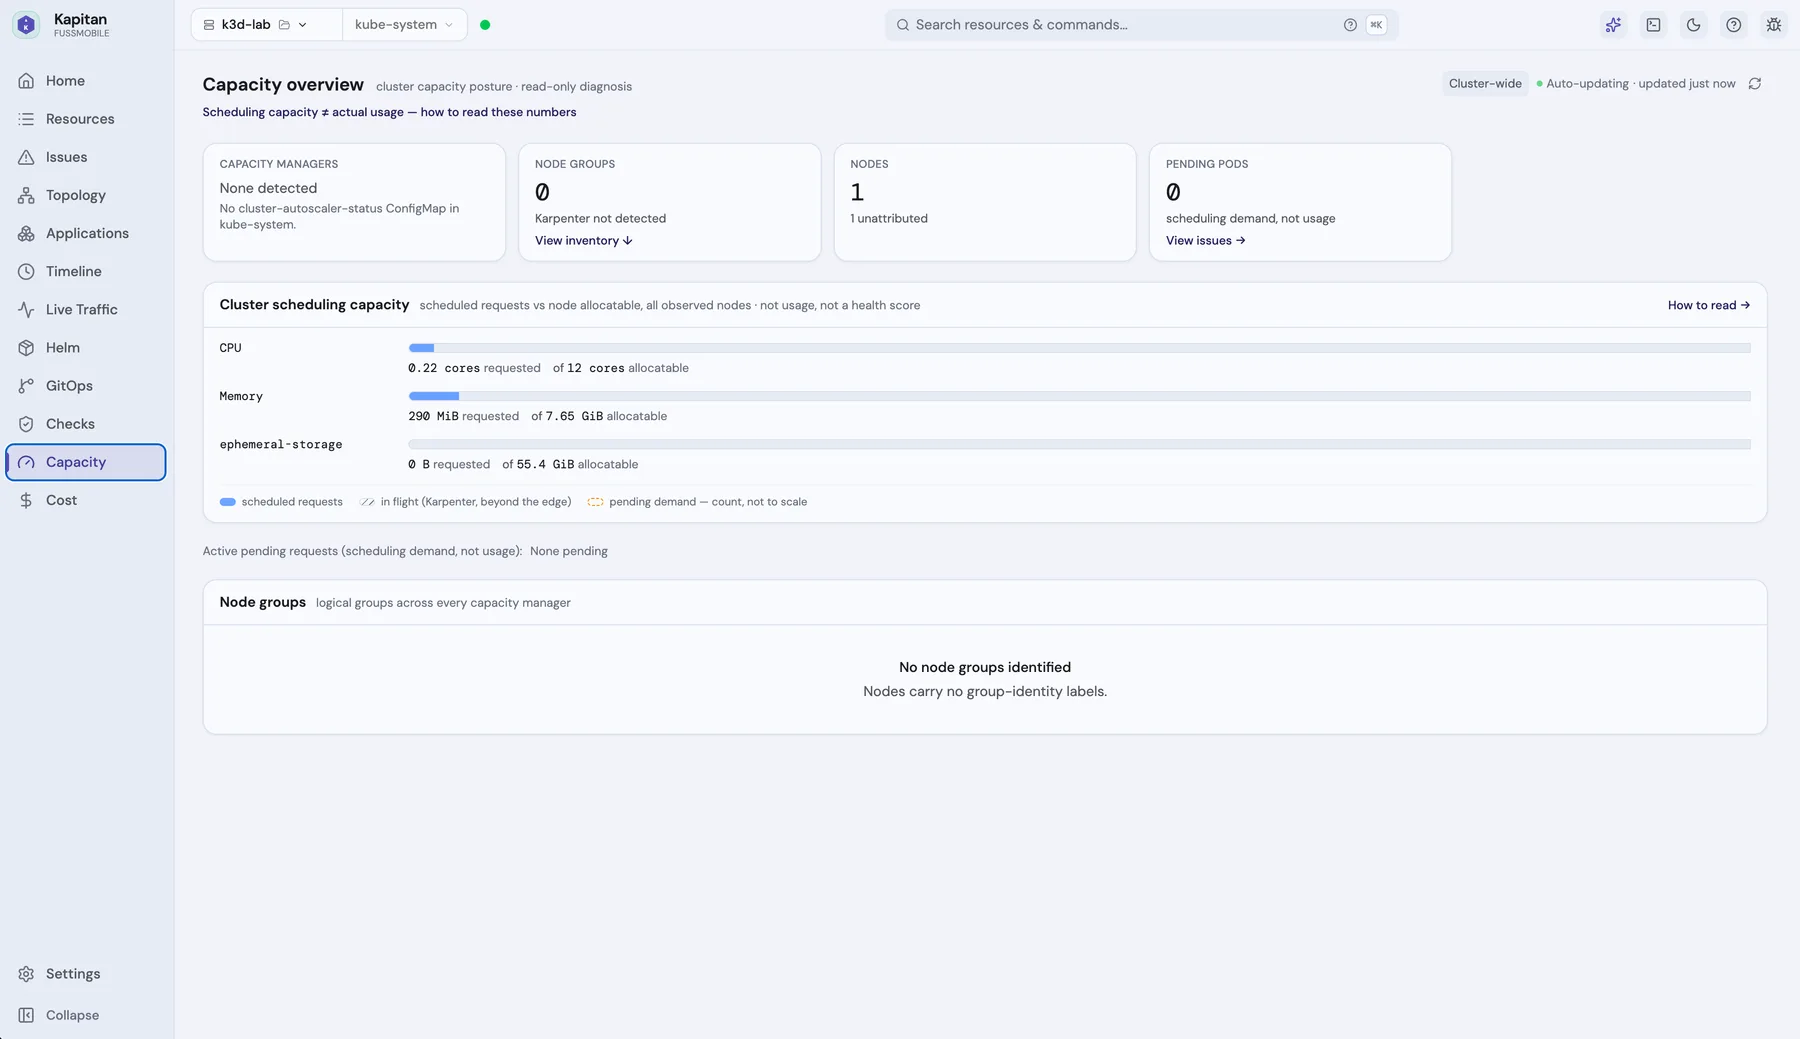
Capacity you can reason about
Scheduling capacity, real usage, and pending demand shown separately — so "do we have room" has an honest answer instead of one misleading percentage.
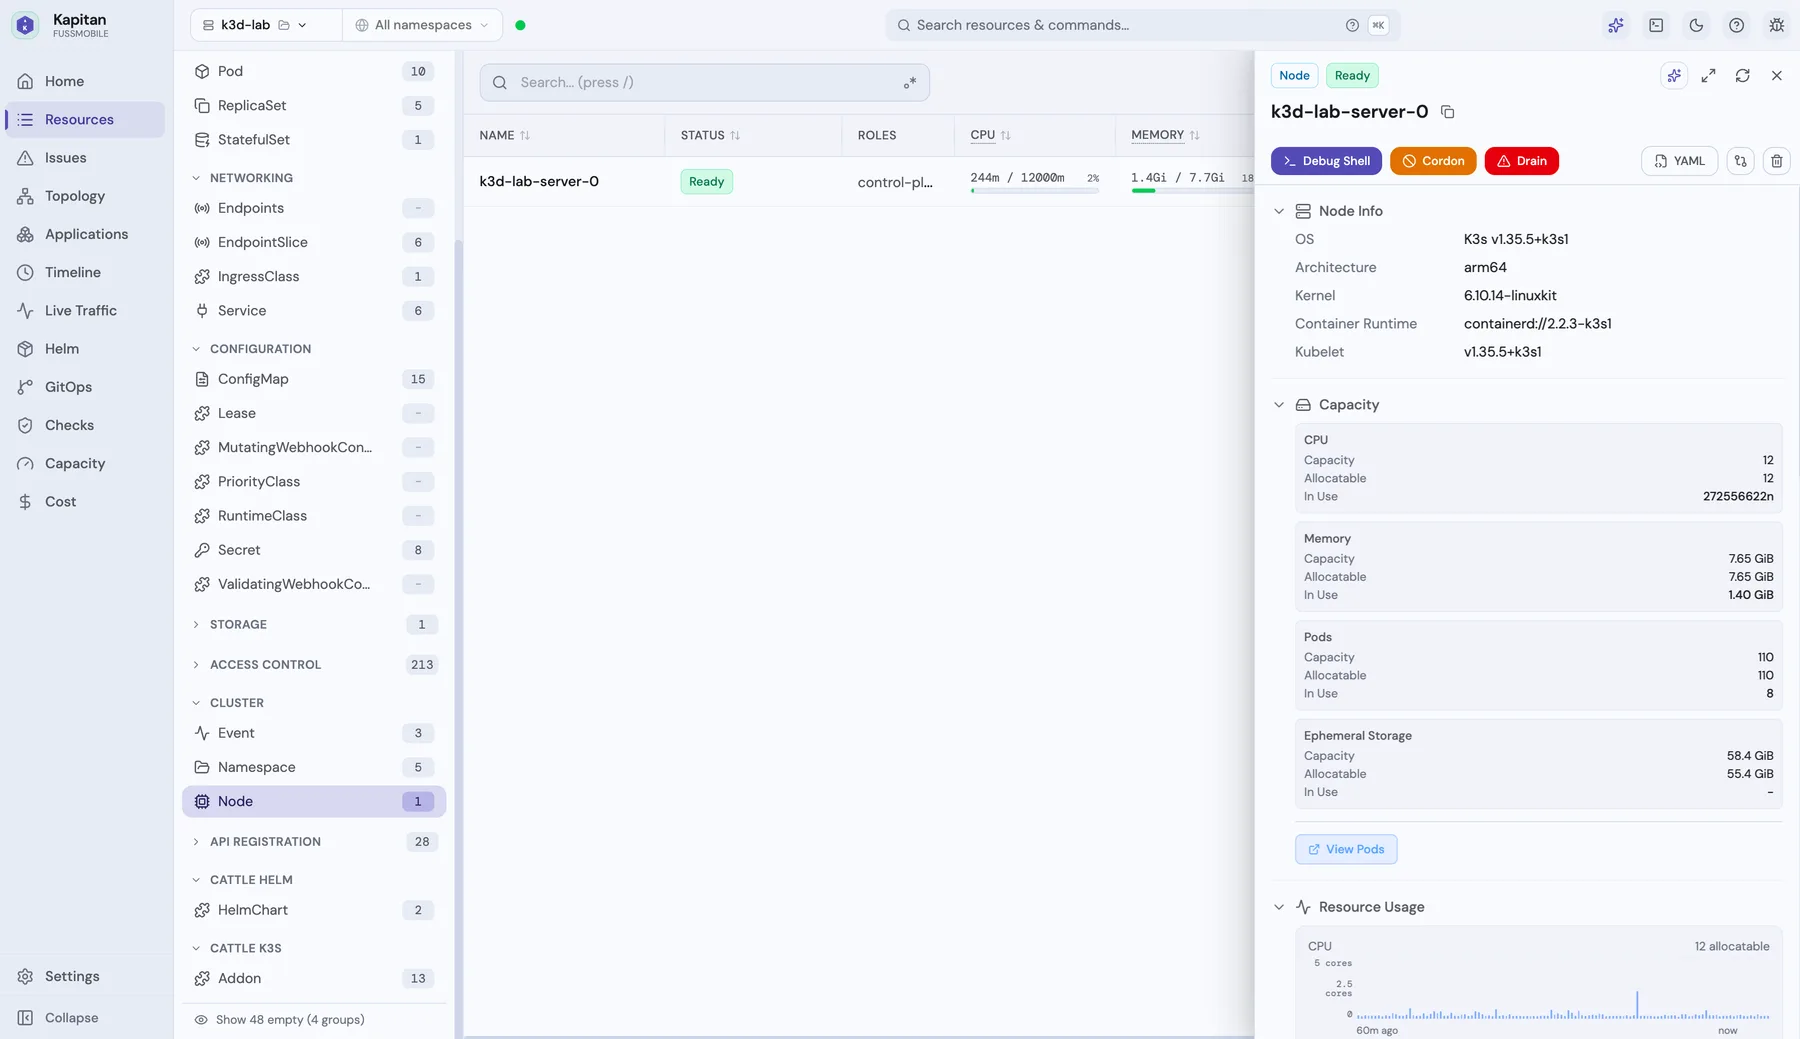
Down to the node, when you need it
One browsable inventory of everything in the cluster, with node-level detail — kernel, container runtime, live capacity — and a debug shell a click away.
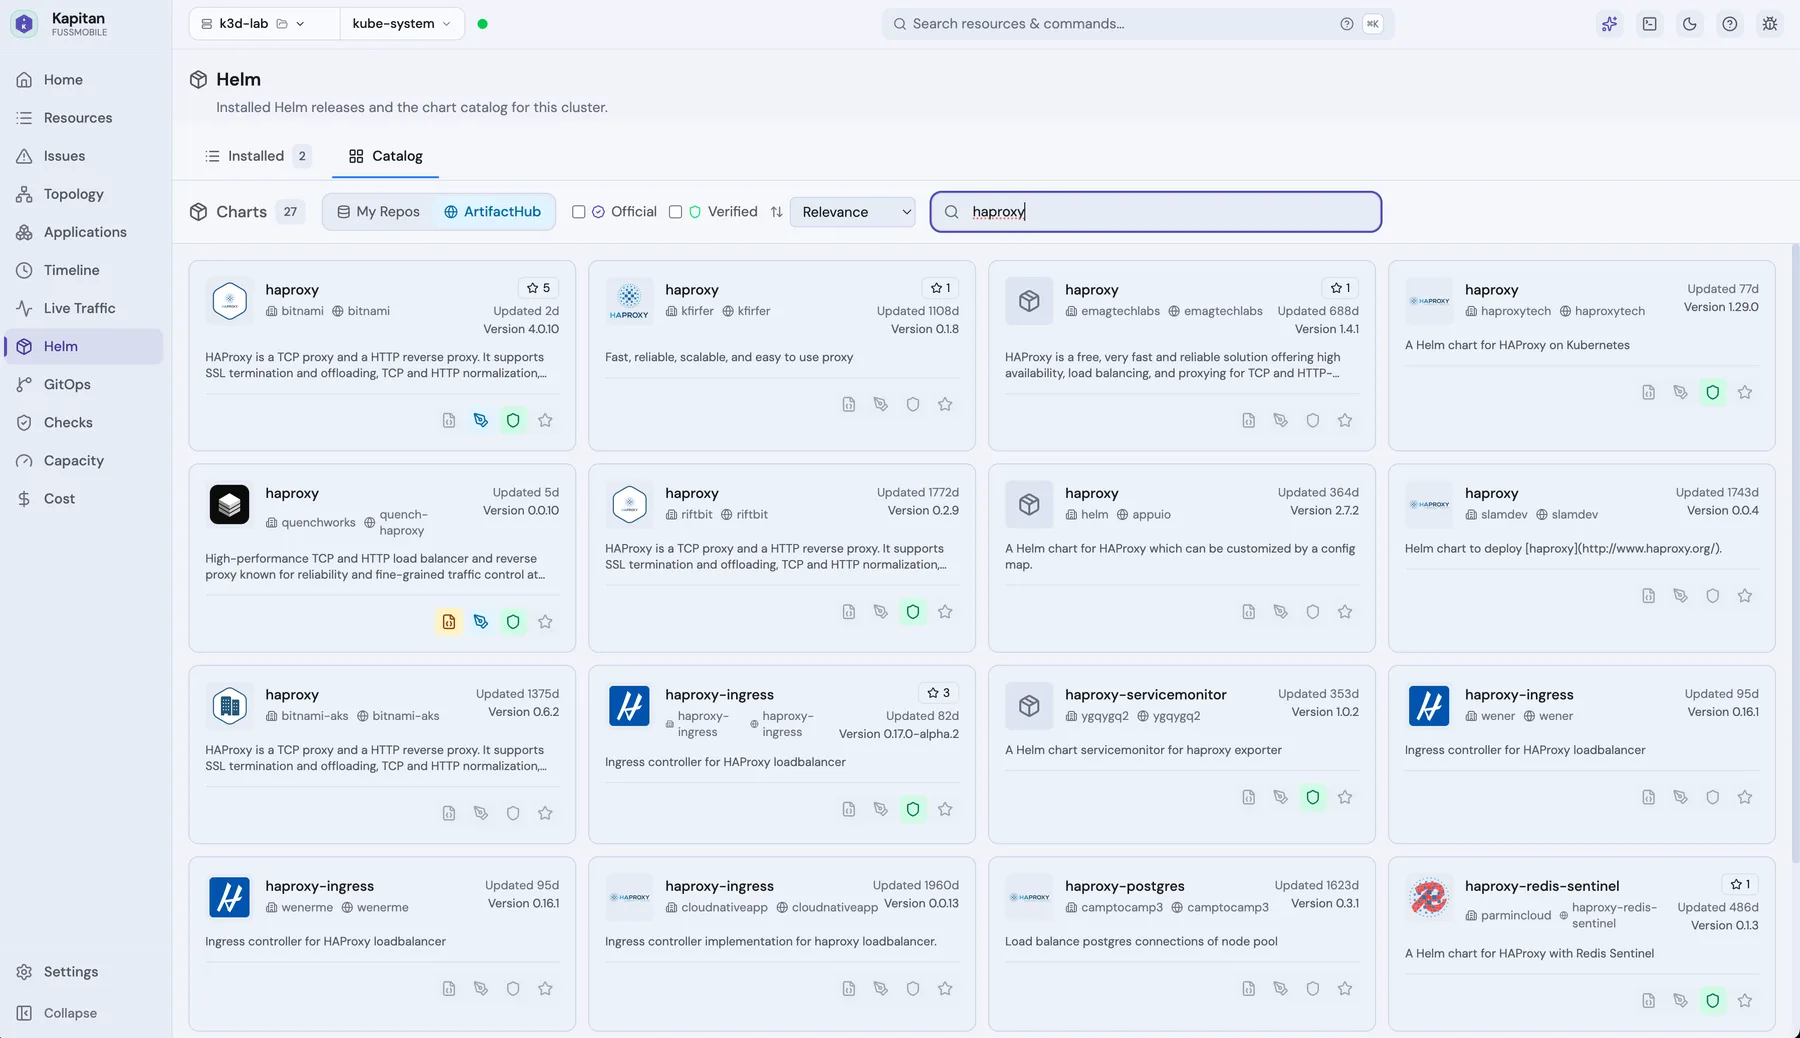
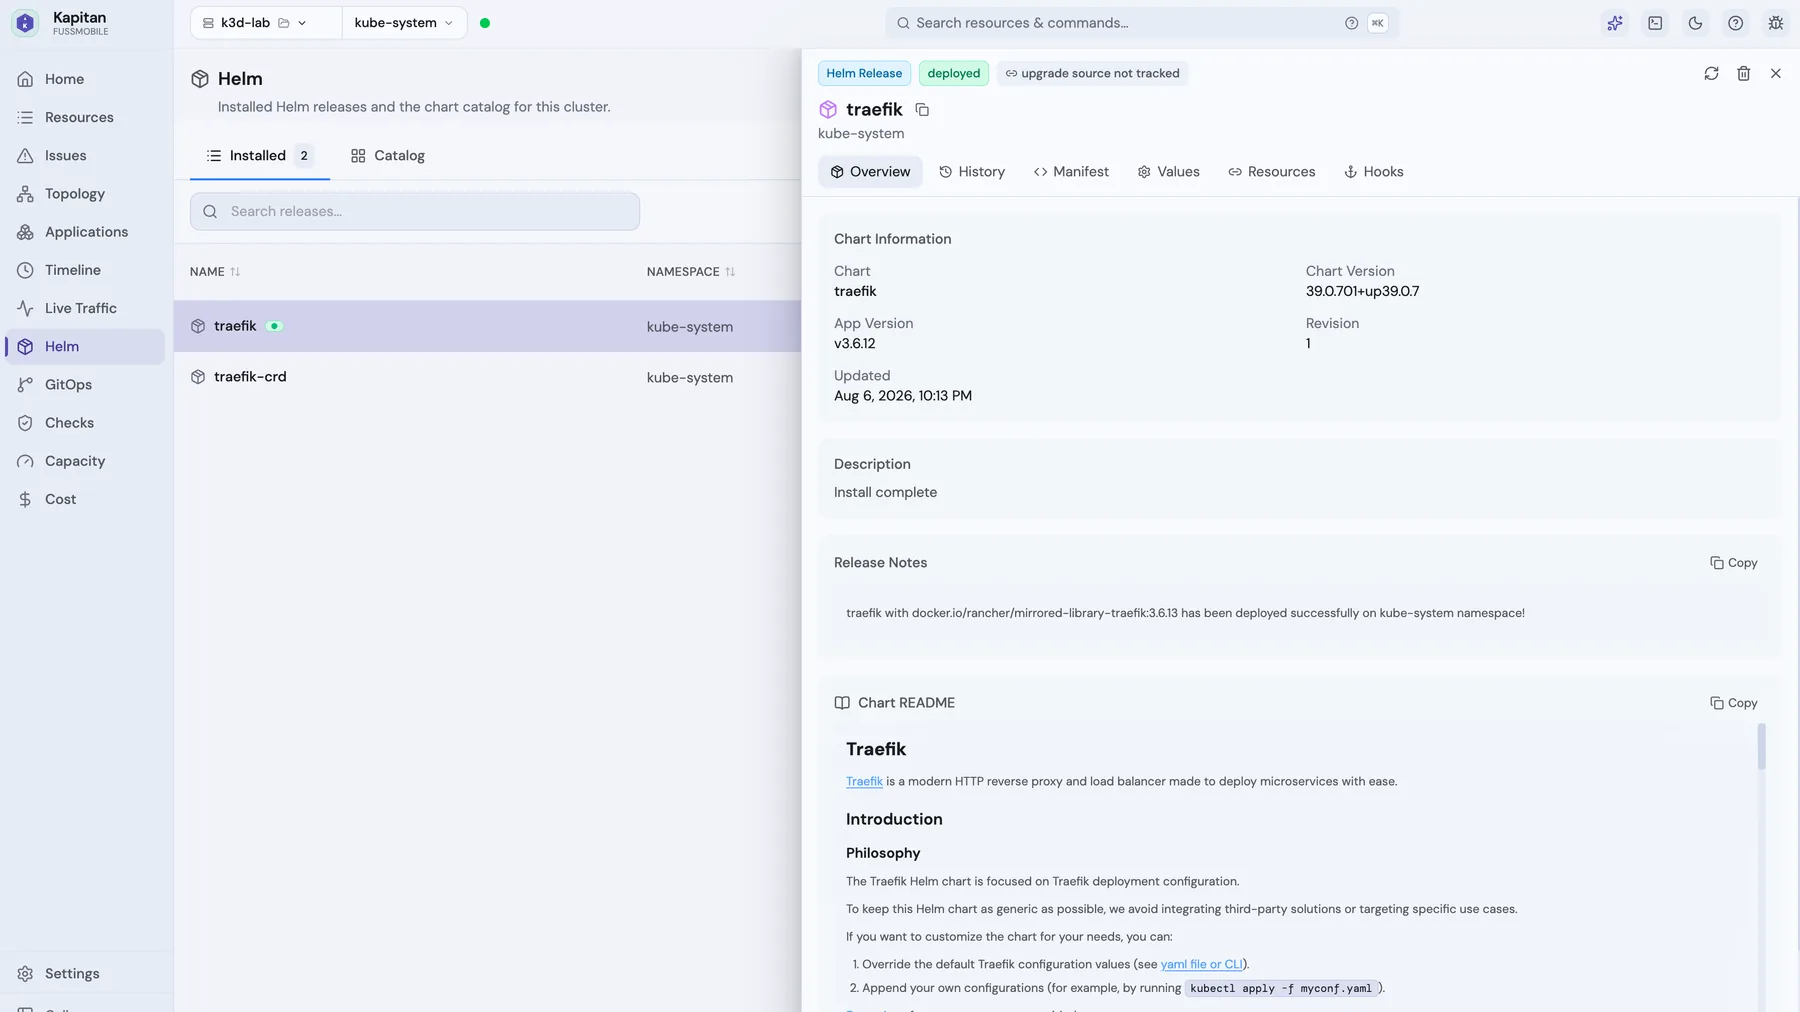
Curated Helm delivery
Browse and install from a searchable chart catalog, then track exactly what shipped, when, and on which chart version — no separate tooling required.
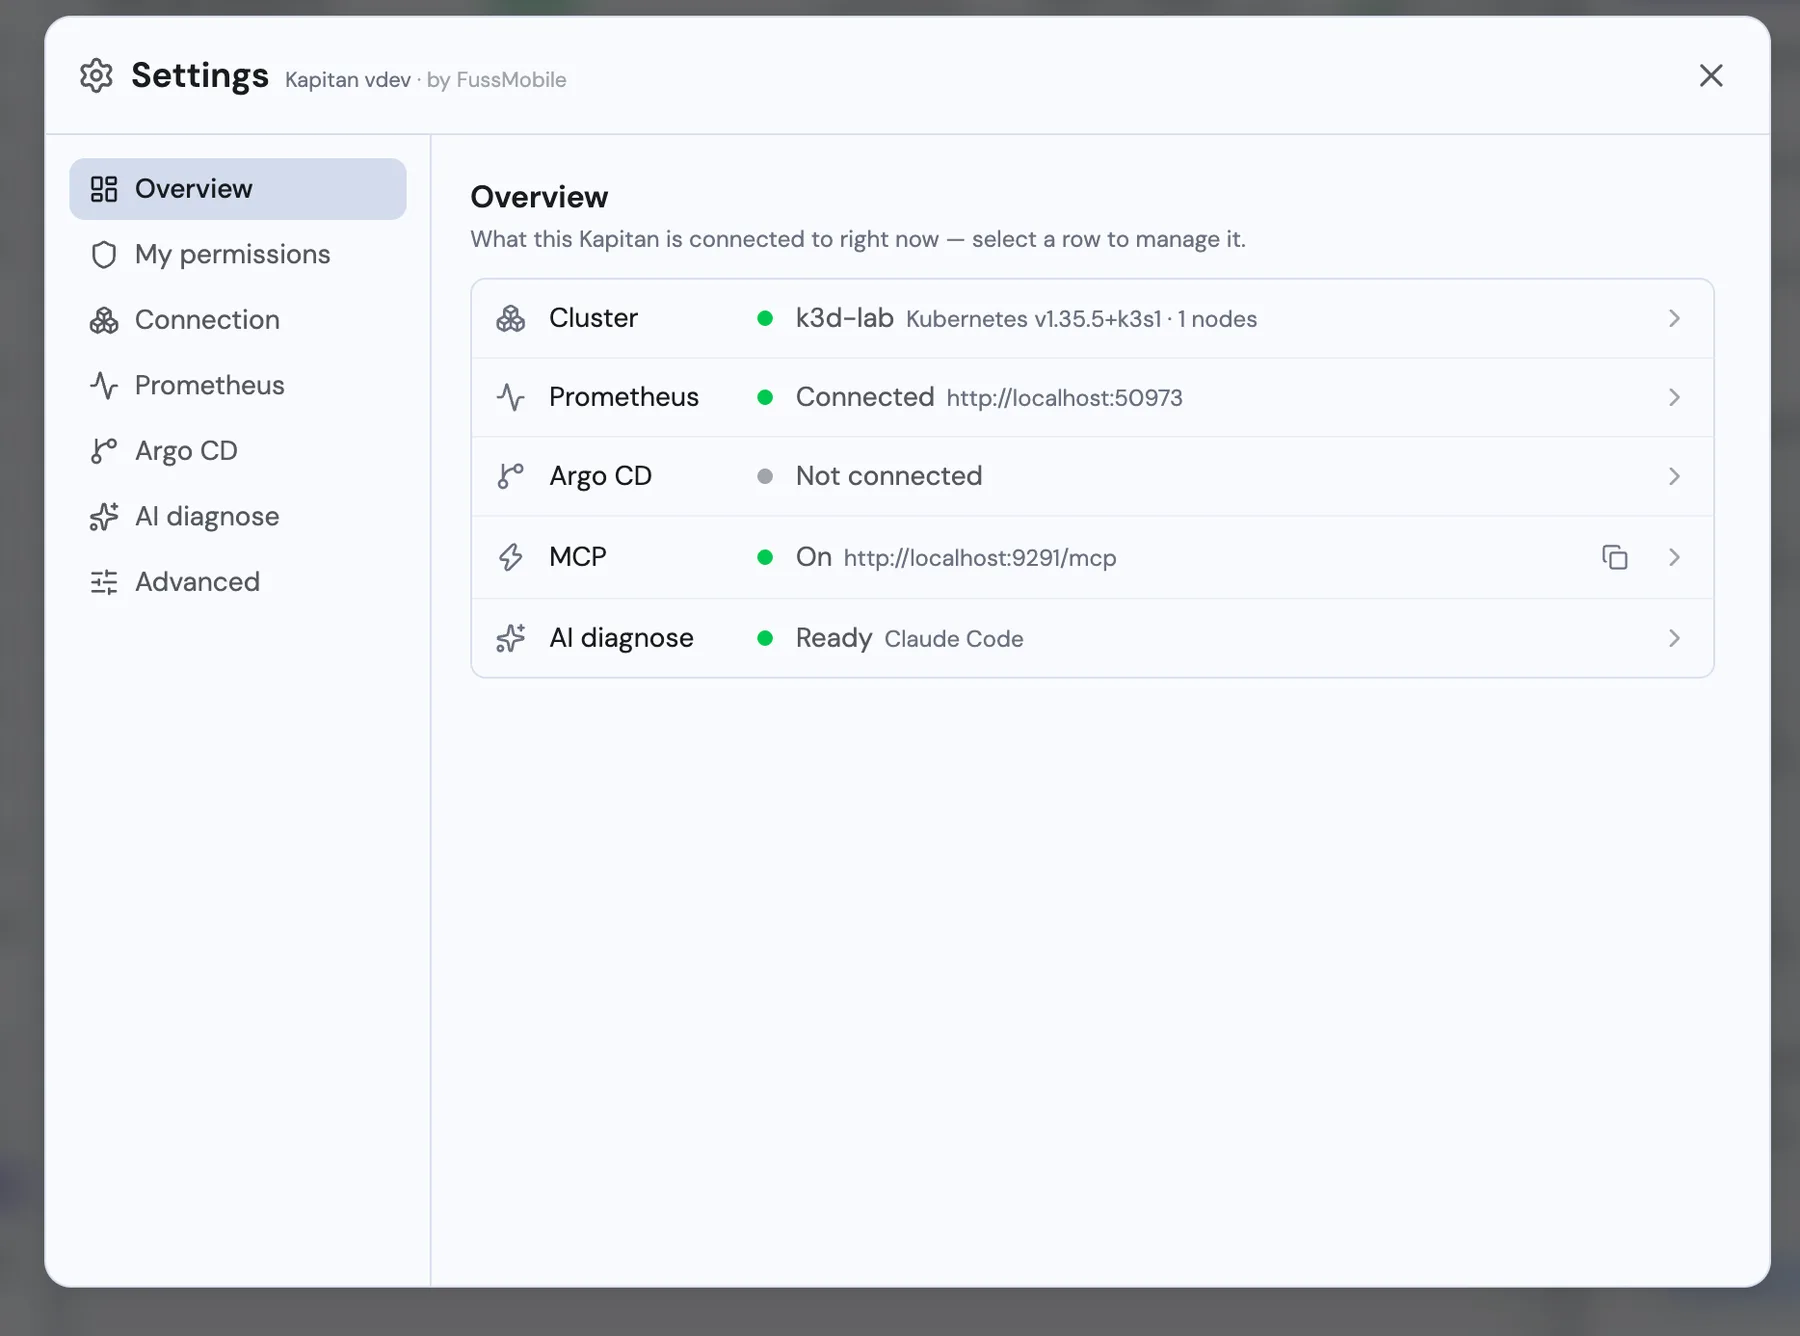
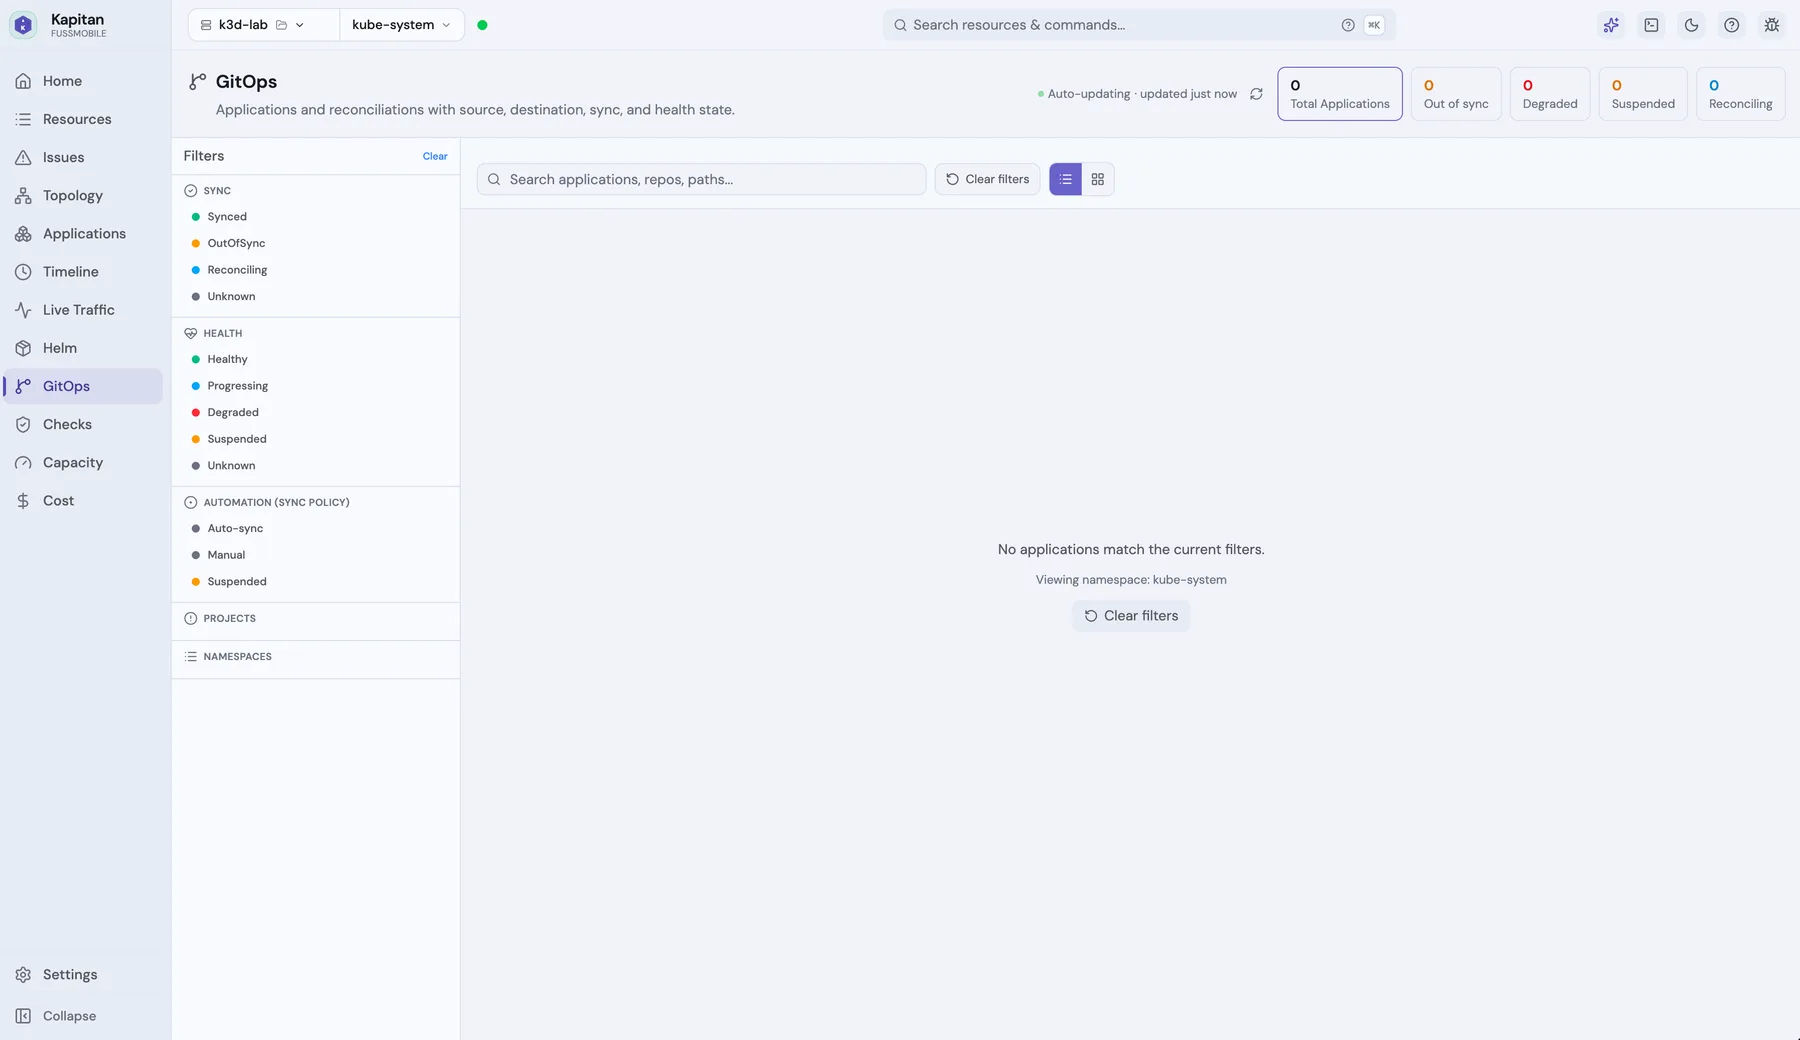
Bring your existing stack
Kapitan connects to what you already run instead of replacing it — point it at your metrics source and delivery pipeline and it's live.
Reference deployment
Deployed across the world's leading cruise lines.
Kapitan has been the managed Kubernetes platform for Norwegian Cruise Line Holdings since 2022 — serving three independent cruise brands across a global fleet of 66 ships.
Norwegian Cruise Line
FussMobile's original cruise line client. Kapitan manages the full technology estate across the NCL fleet — from shipboard edge clusters to mobile application infrastructure.
Regent Seven Seas Cruises
The world's leading luxury cruise line. Kapitan provides managed Kubernetes operations across the Regent fleet with the same zero-incident reliability as the broader program.
Oceania Cruises
The finest cuisine at sea. Kapitan delivers managed edge infrastructure for the Oceania fleet — same platform, same operational standards, same outcome guarantee.
“Four years. Three brands. Sixty-six ships.
Zero production incidents.”
Get in touch
Let's talk about your environment.
Whether you're evaluating managed Kubernetes for a new deployment, looking to migrate an existing estate, or exploring a specific capability — we respond to every inquiry directly.
FussMobile LLC · Hoboken, NJ
[email protected]